Overview
This project started when I needed to make changes to multiple SSL profiles on numerous F5s. While the task is quite straight forward of changing the defaults-from command on multiple SSL profiles the difficulty always comes from the non-technical aspect of change control.
Instead of performing the change on all the SSL profiles on the F5s I needed to do it for different sets of domains. This is a more complex way to do it and keep track over a longer period.
This project grew from the simple configuration generator into something that can now perform checks config and rollback to all F5s and multiple domains.
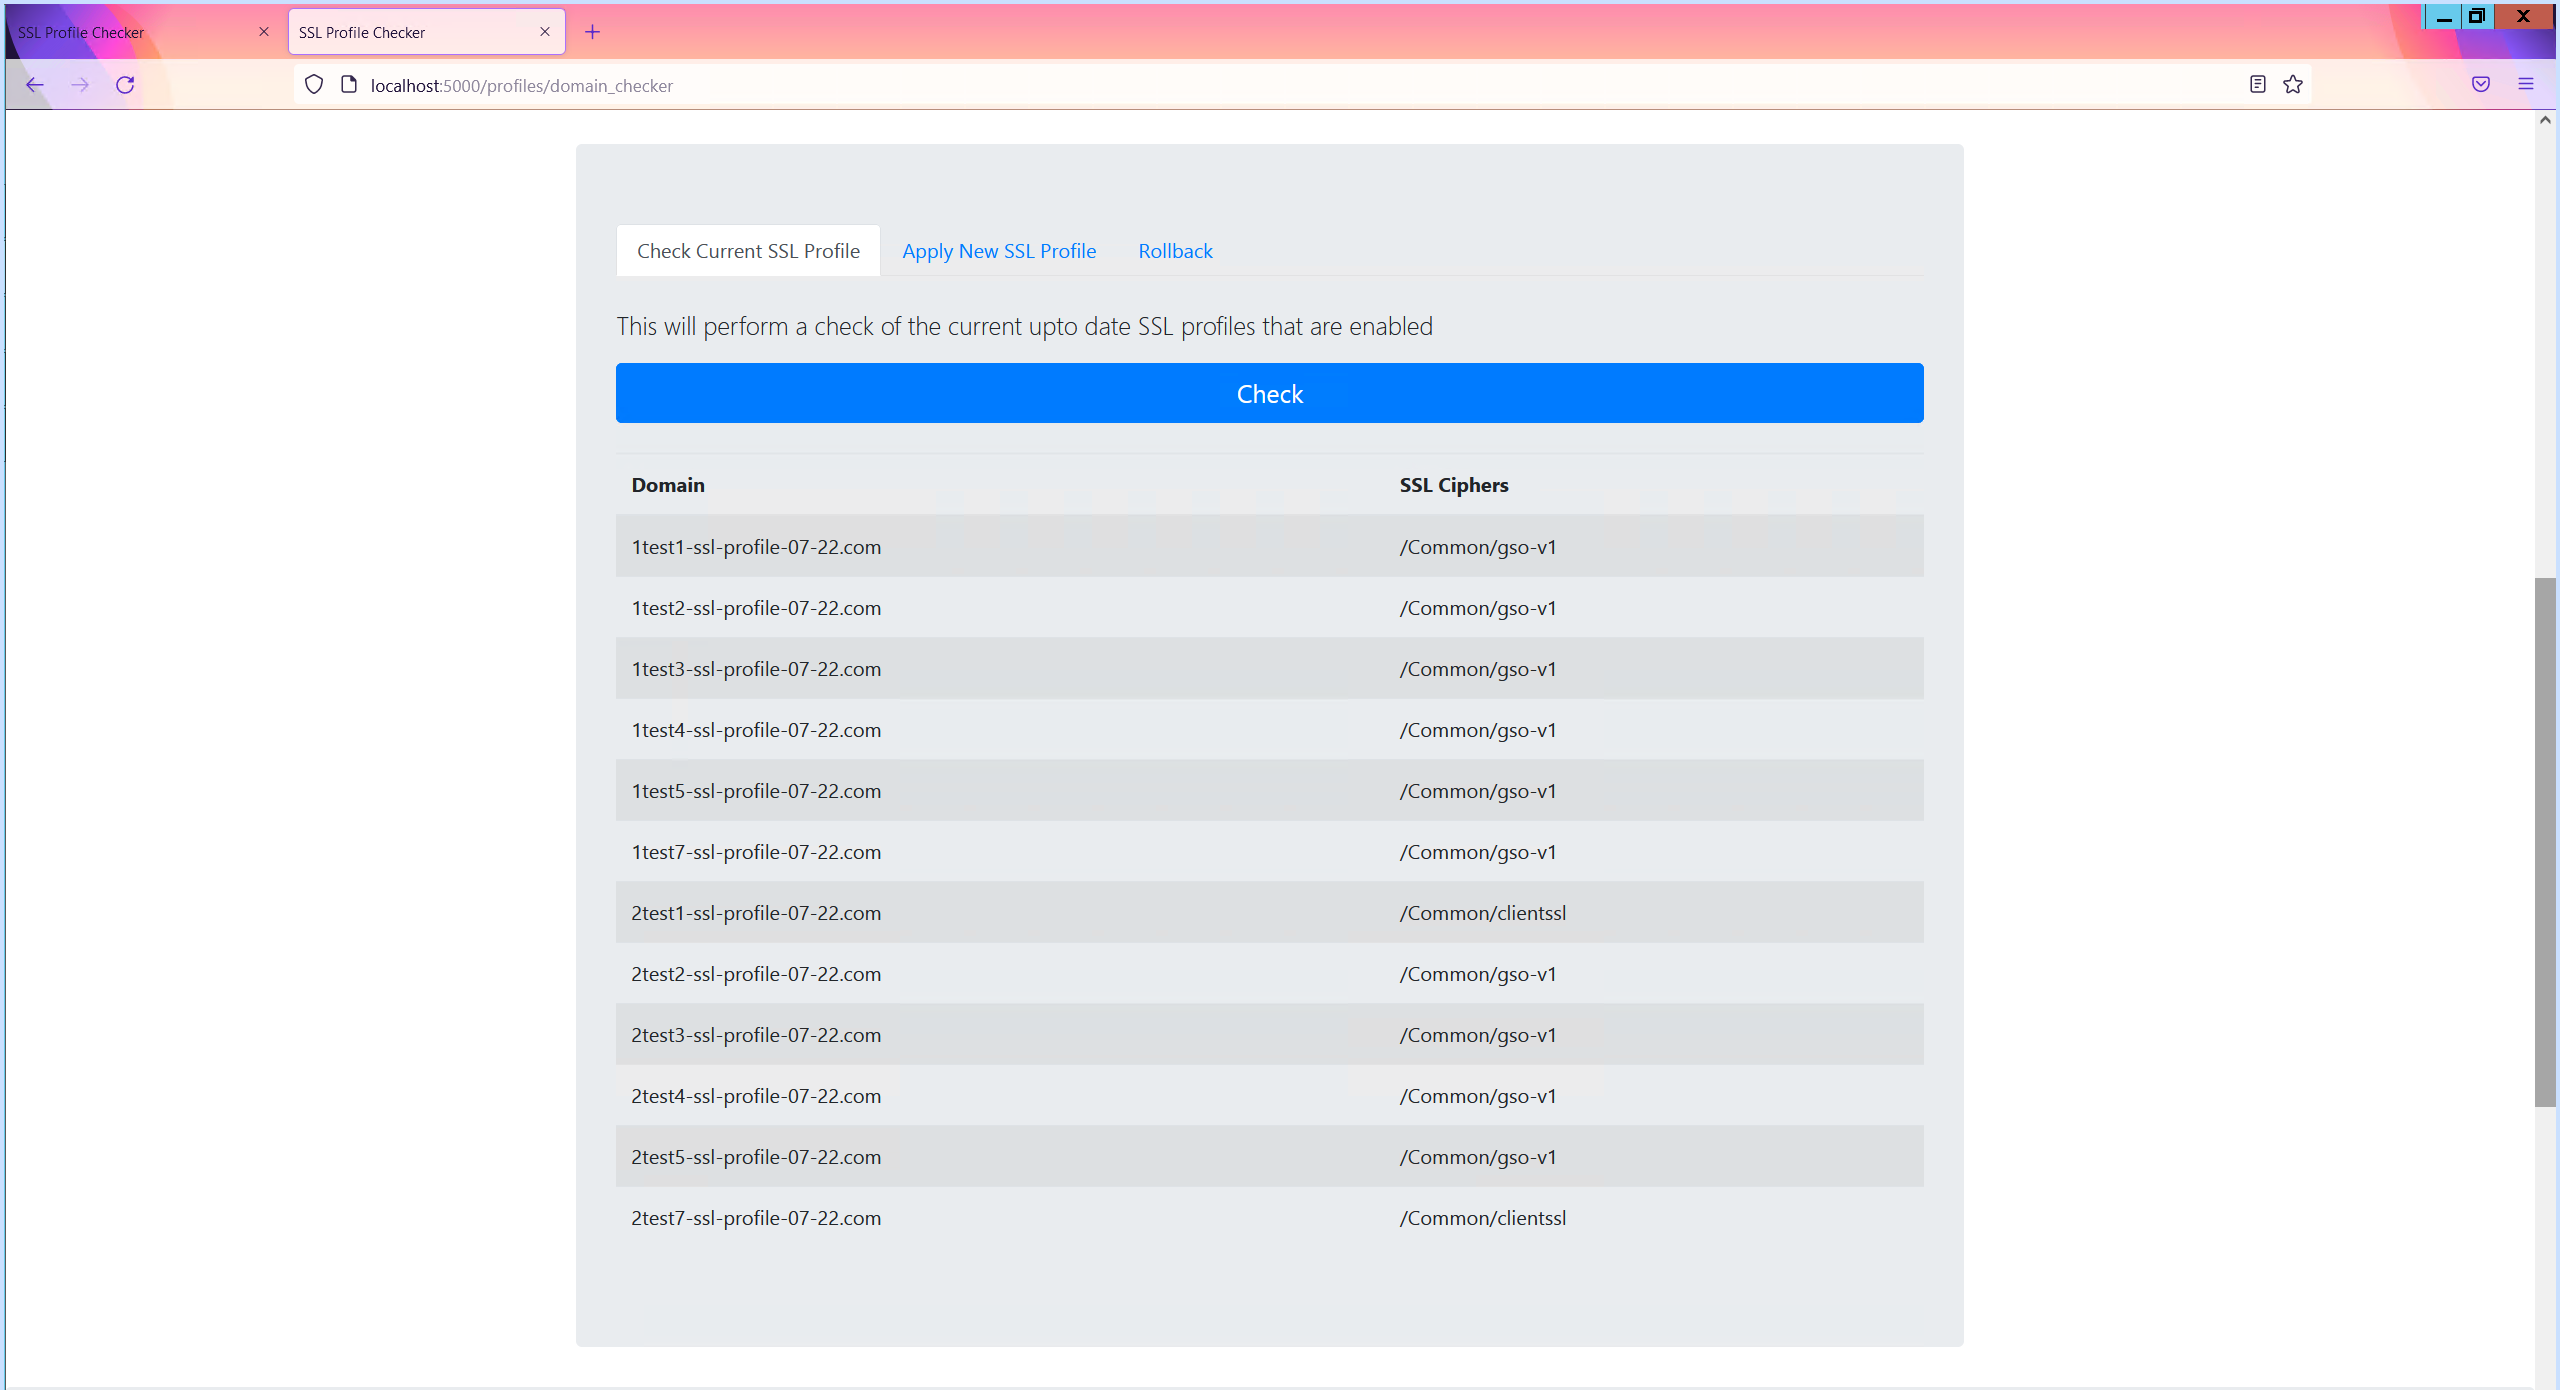
Start with the dashboard below, then follow the project from its first configuration generator to the final workflows. Expand a screenshot collection when you want to explore the interface in detail.
The current functionality is…
- F5 SSL Profiling checking, changing and rolling back to original
- Creating an SSL certificate; getting that signed by a CA and uploading it on the F5.
- Adding to the SSL creation adding a VIP, and members to the pool
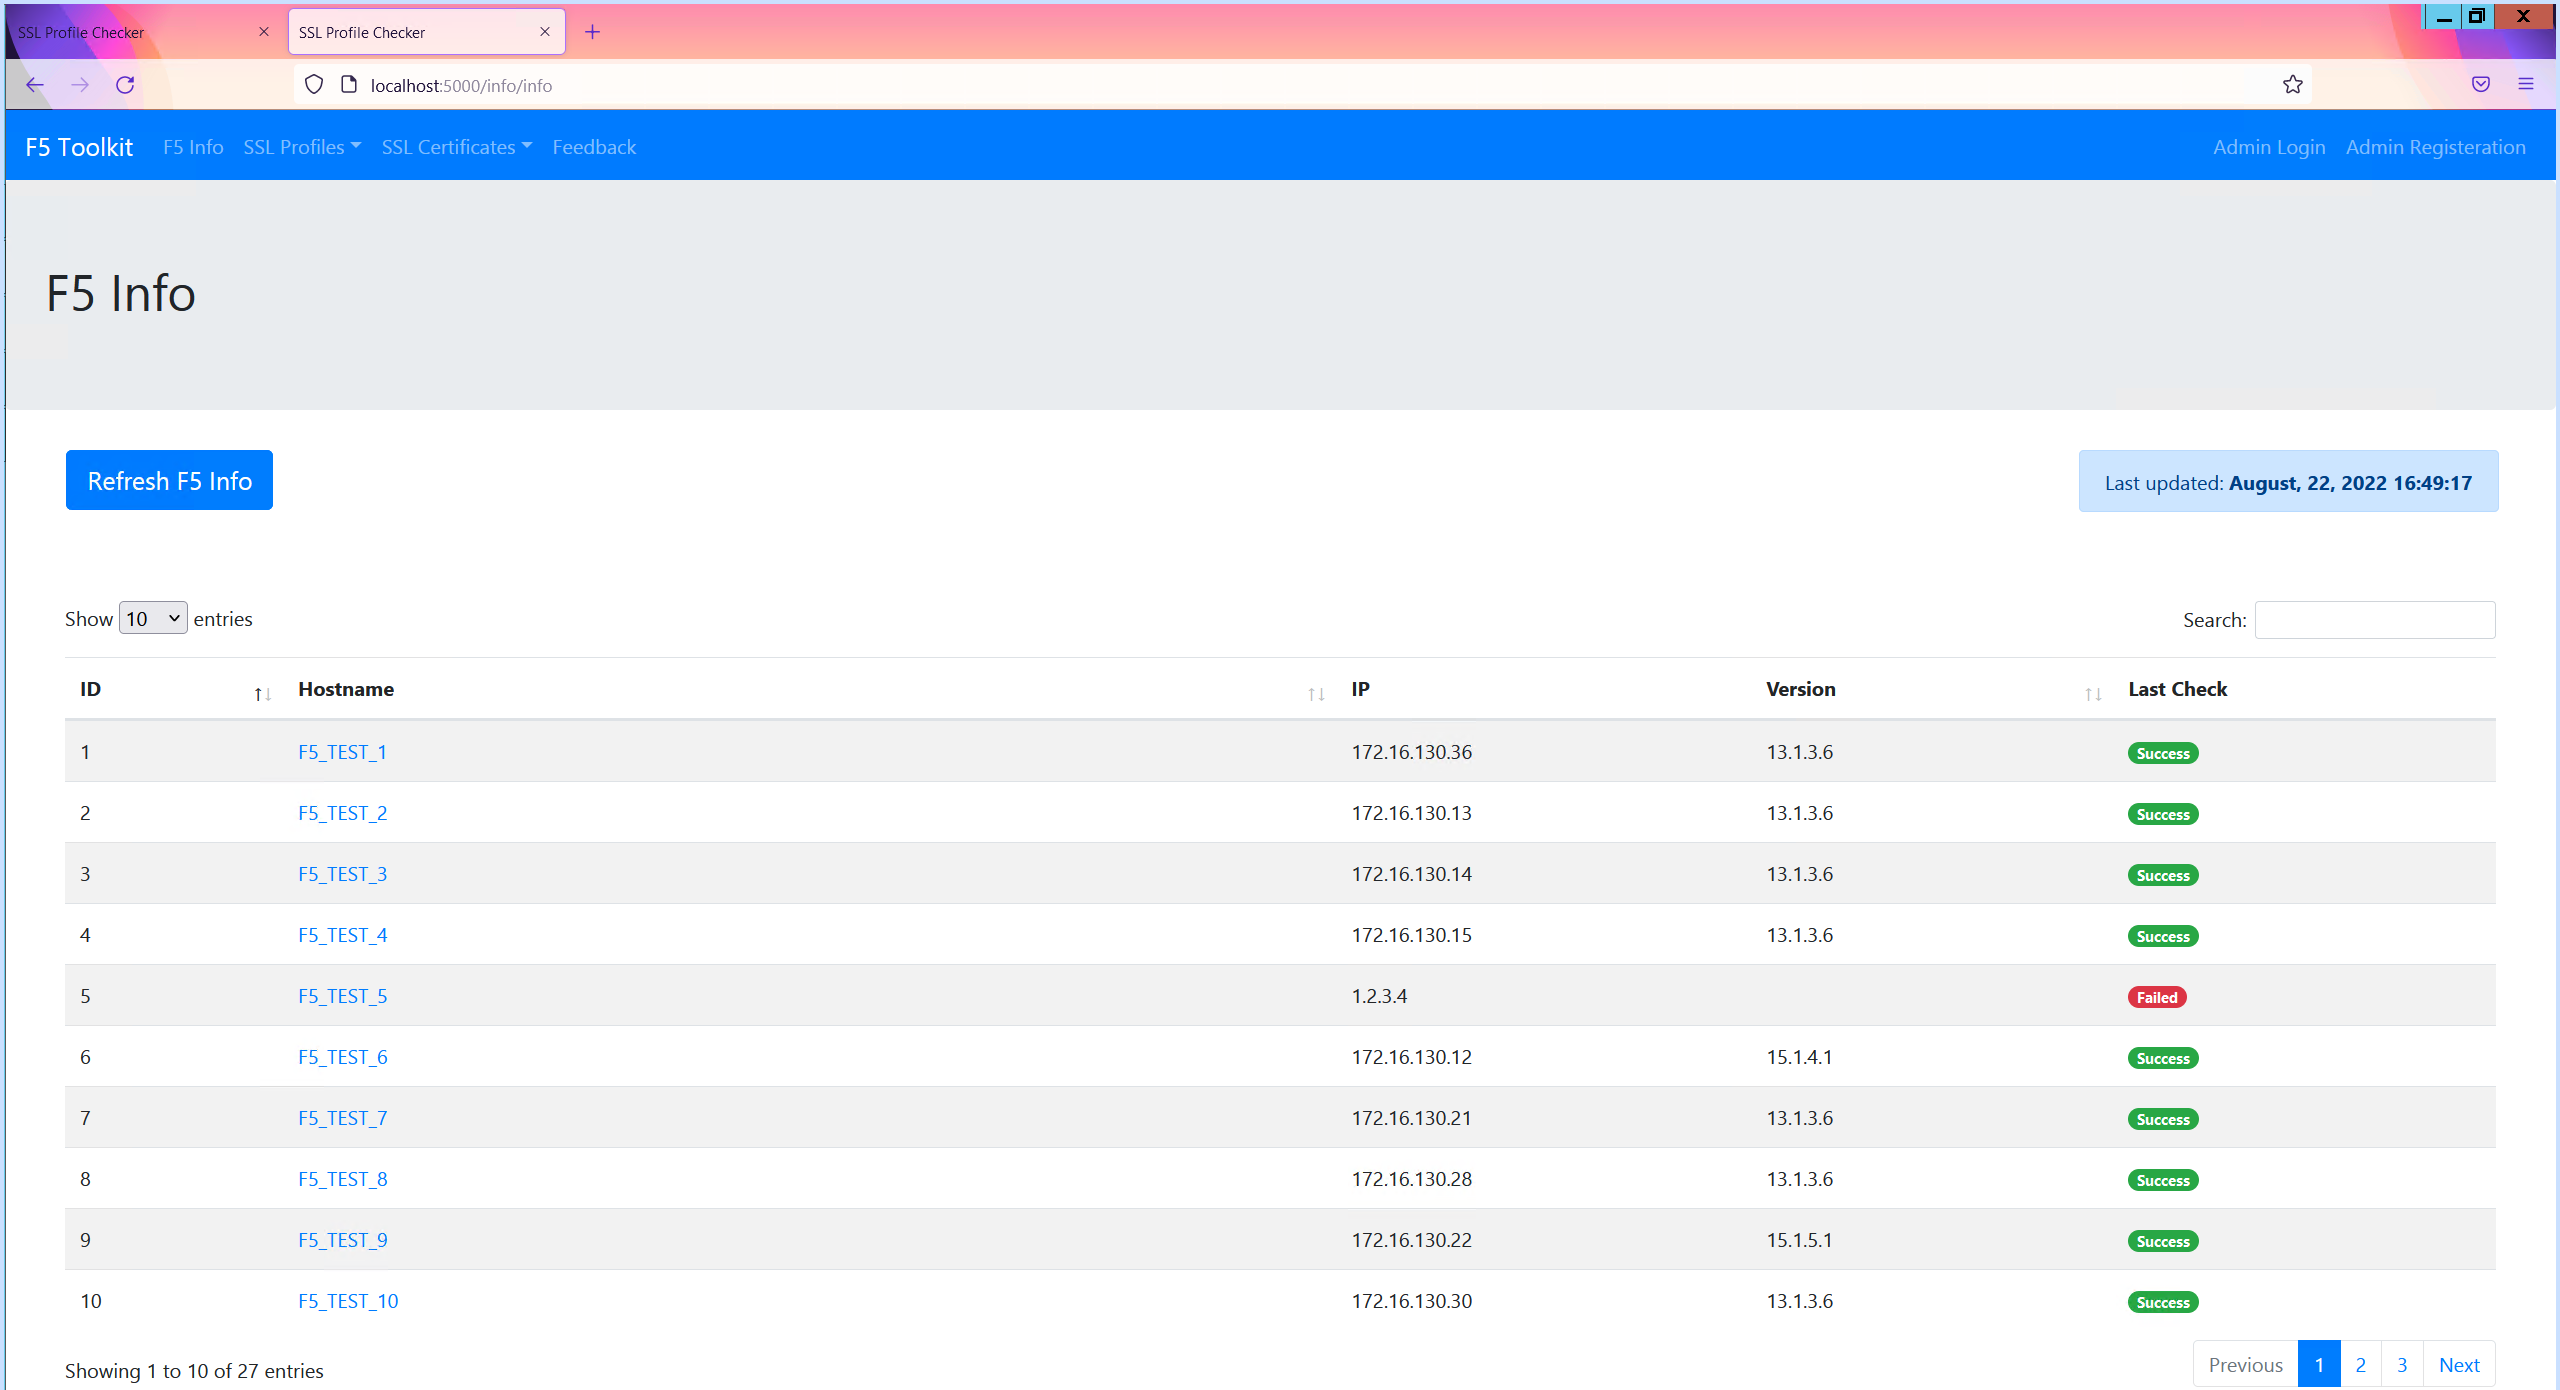
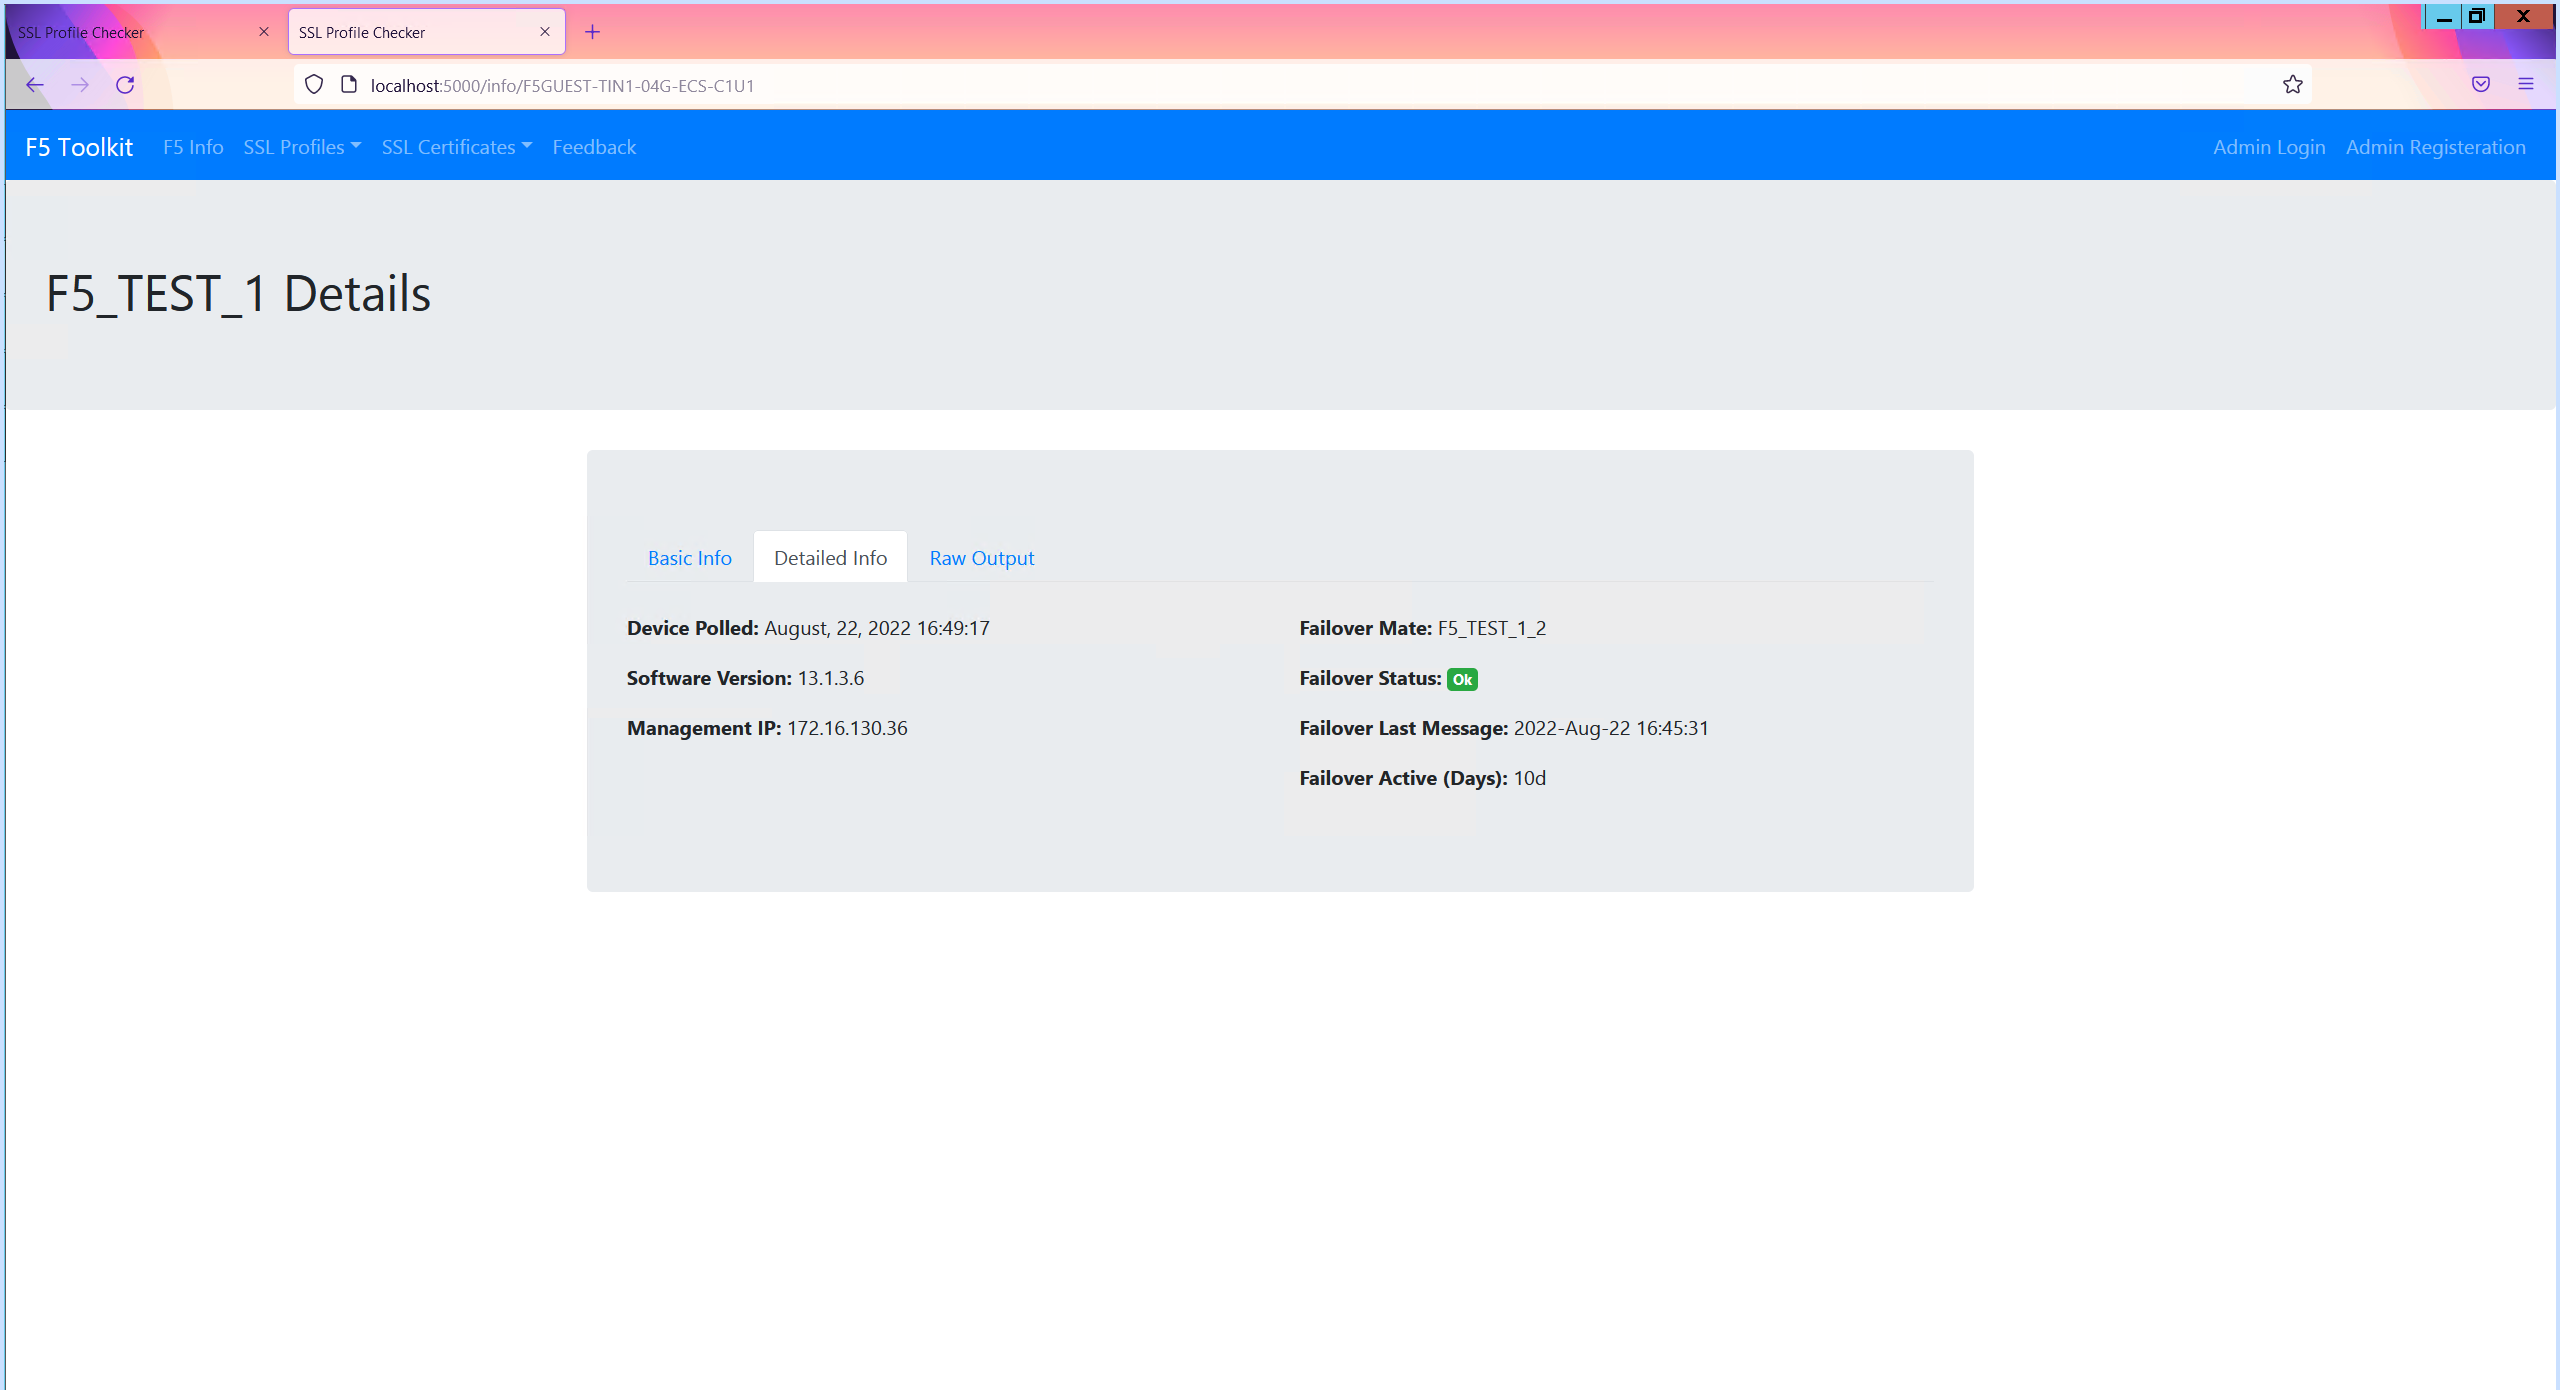
- Gathering F5 info; failover info, management IP, software versions
- Proving feedback (to me)
- Login page (currently only for downloading the feedback database table)
Explore more dashboard views5 screenshots
Additional views of the latest dashboard, including domain checks and F5 details.
1. The configuration generator
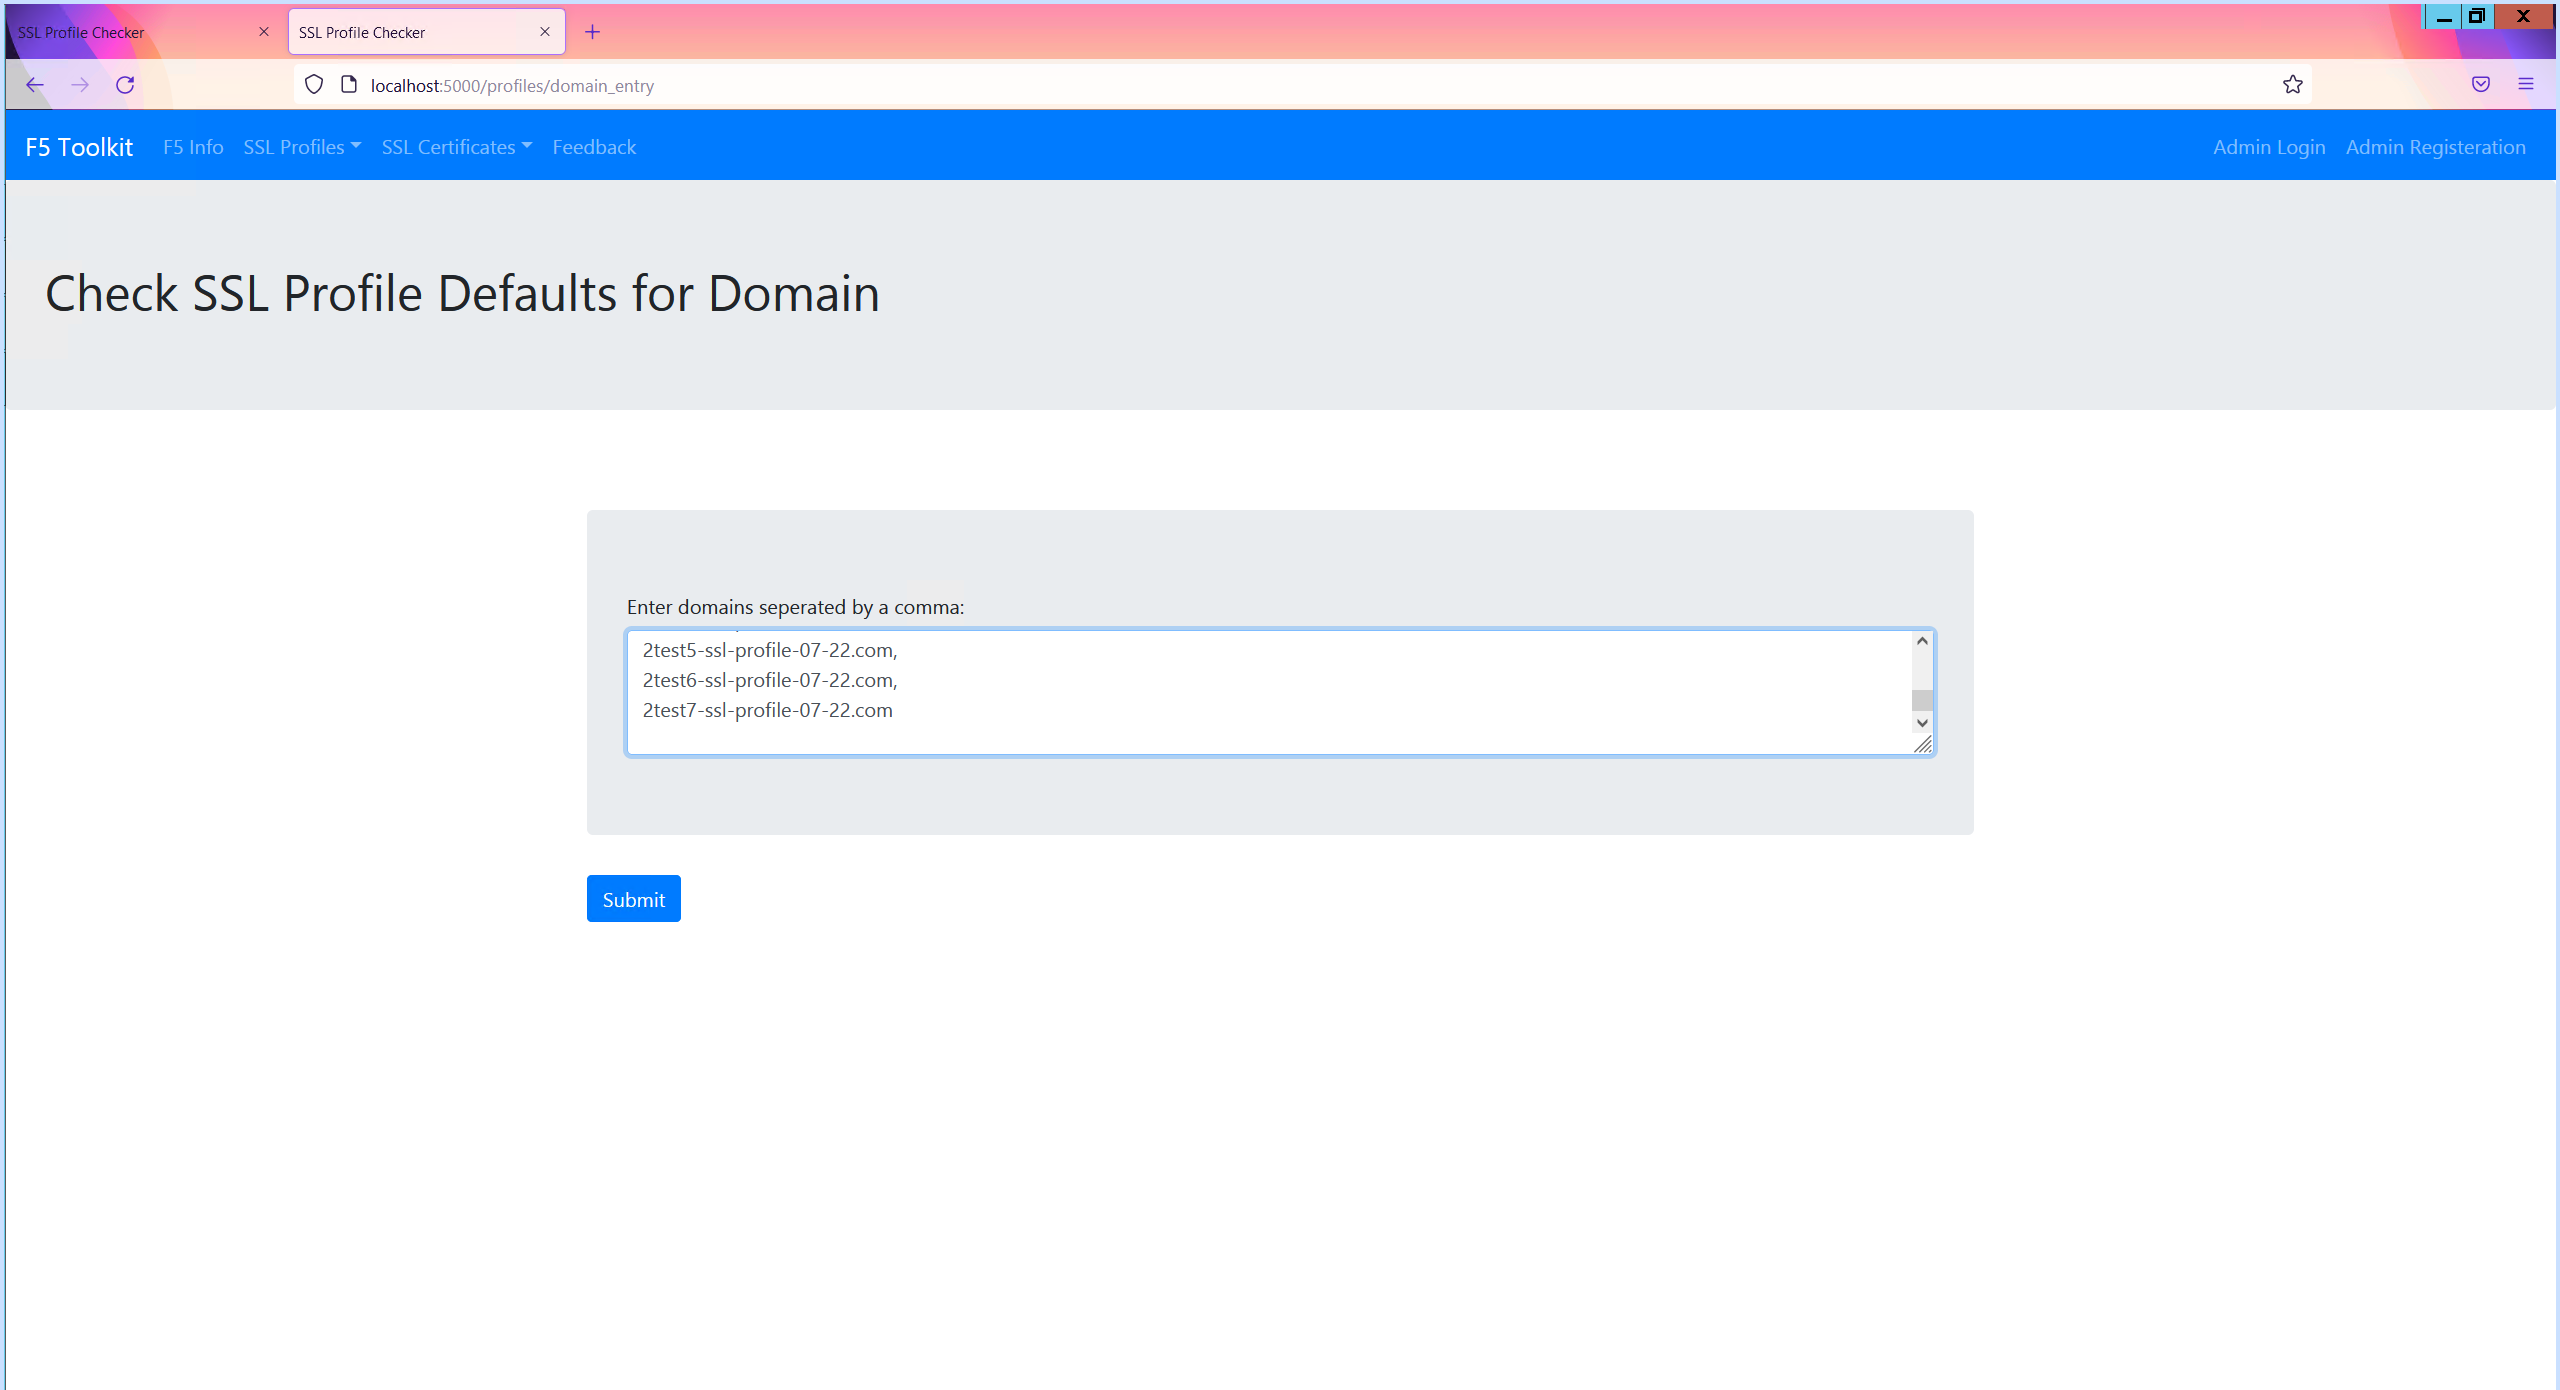
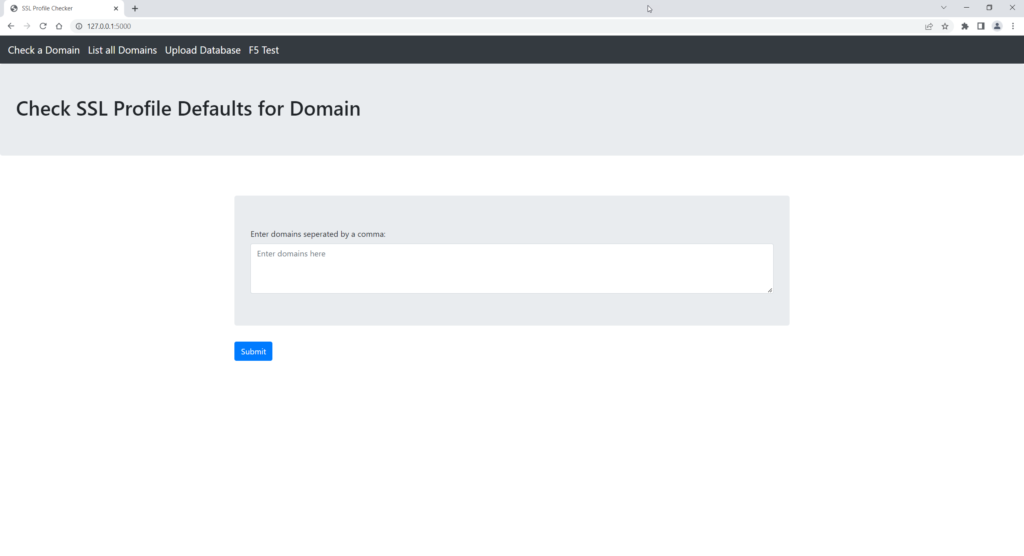
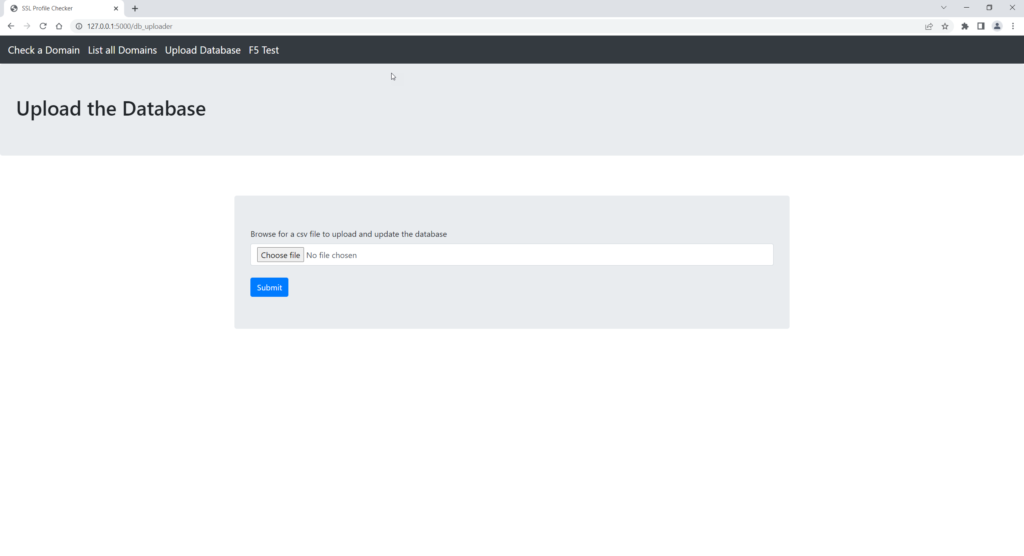
This first started out as just a basic configuration generator. Nothing too smart other than using a database to check if it’s been done. This database is also manually updated. So, no checks directly on the F5 itself.
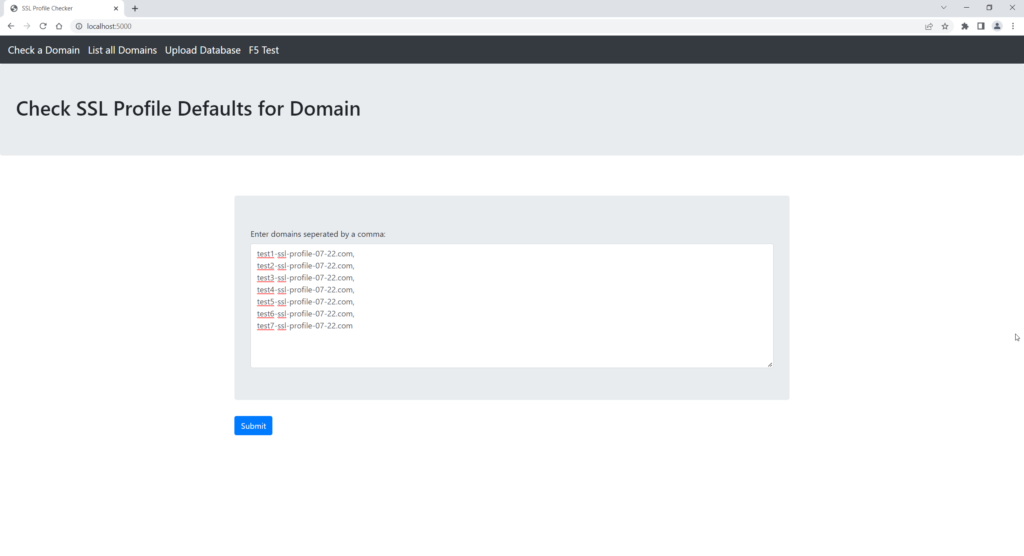
- Enter domain or domains
- Check to see if the SSL profile requires updating
- If so, provide configuration and the name of the F5 that it is required
- The configuration output will be the basic command line to update the defaults from on the SSL profile.
- The user will copy and paste this into the F5 in the usual manual process
See the first configuration generator9 screenshots
Follow the original workflow: load the database, select domains and review the generated configuration.
2. The dashboard workflows
SSL Profile Configuration
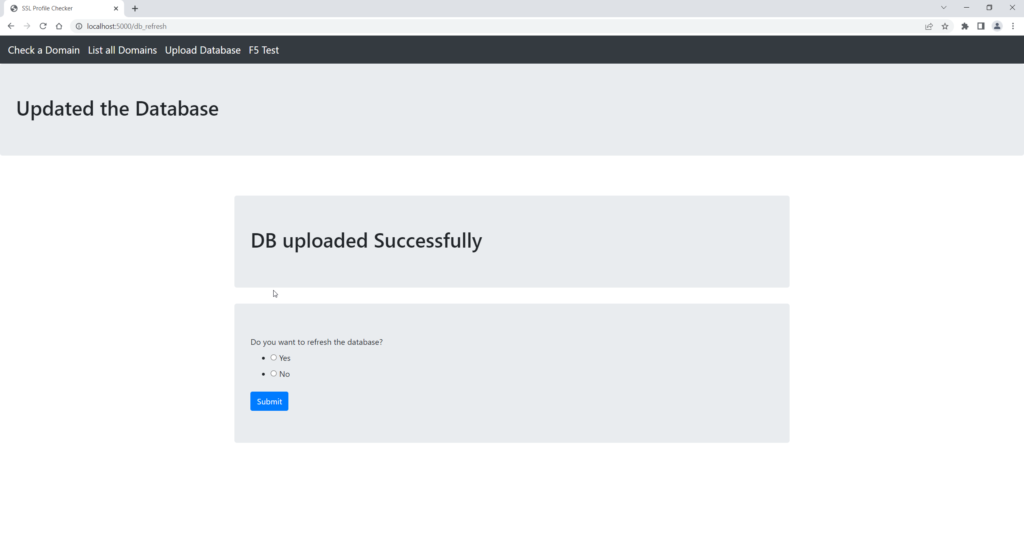
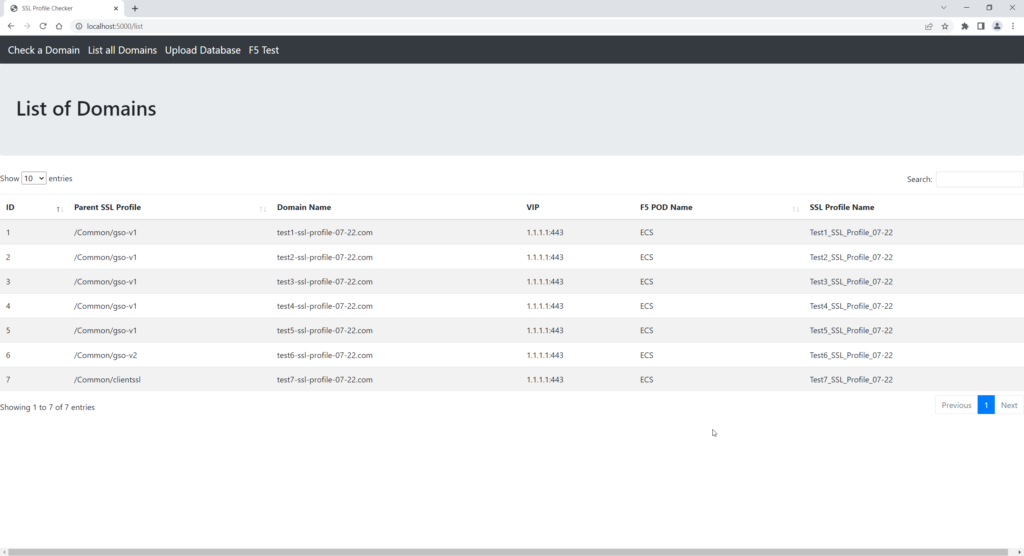
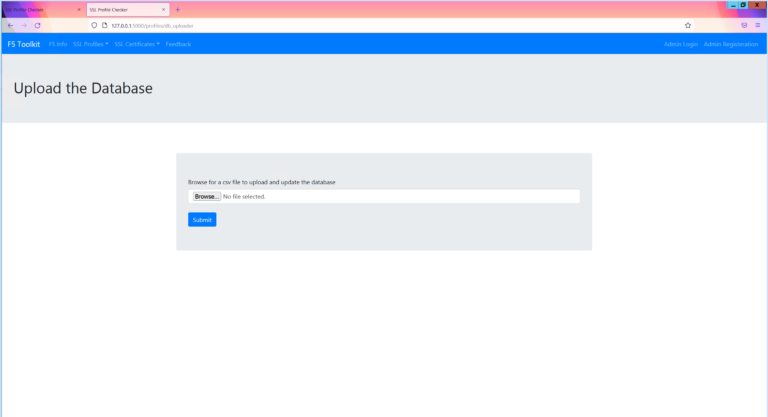
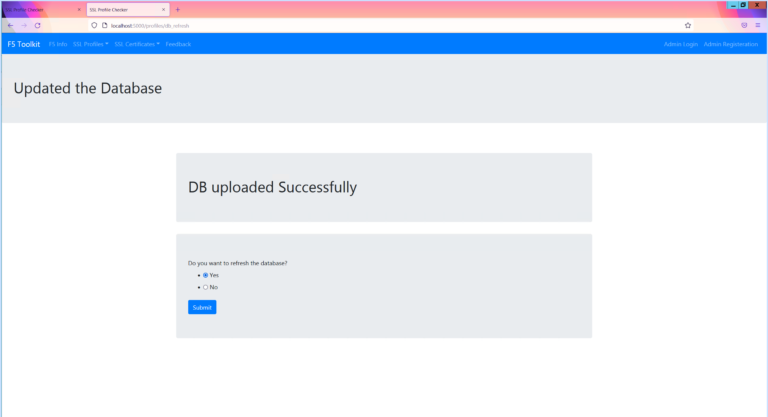
We need to first upload a database that contains;
- Parent SSL Profile Name
- Domain
- VIP
- F5 POD Name
- SSL Profile Name
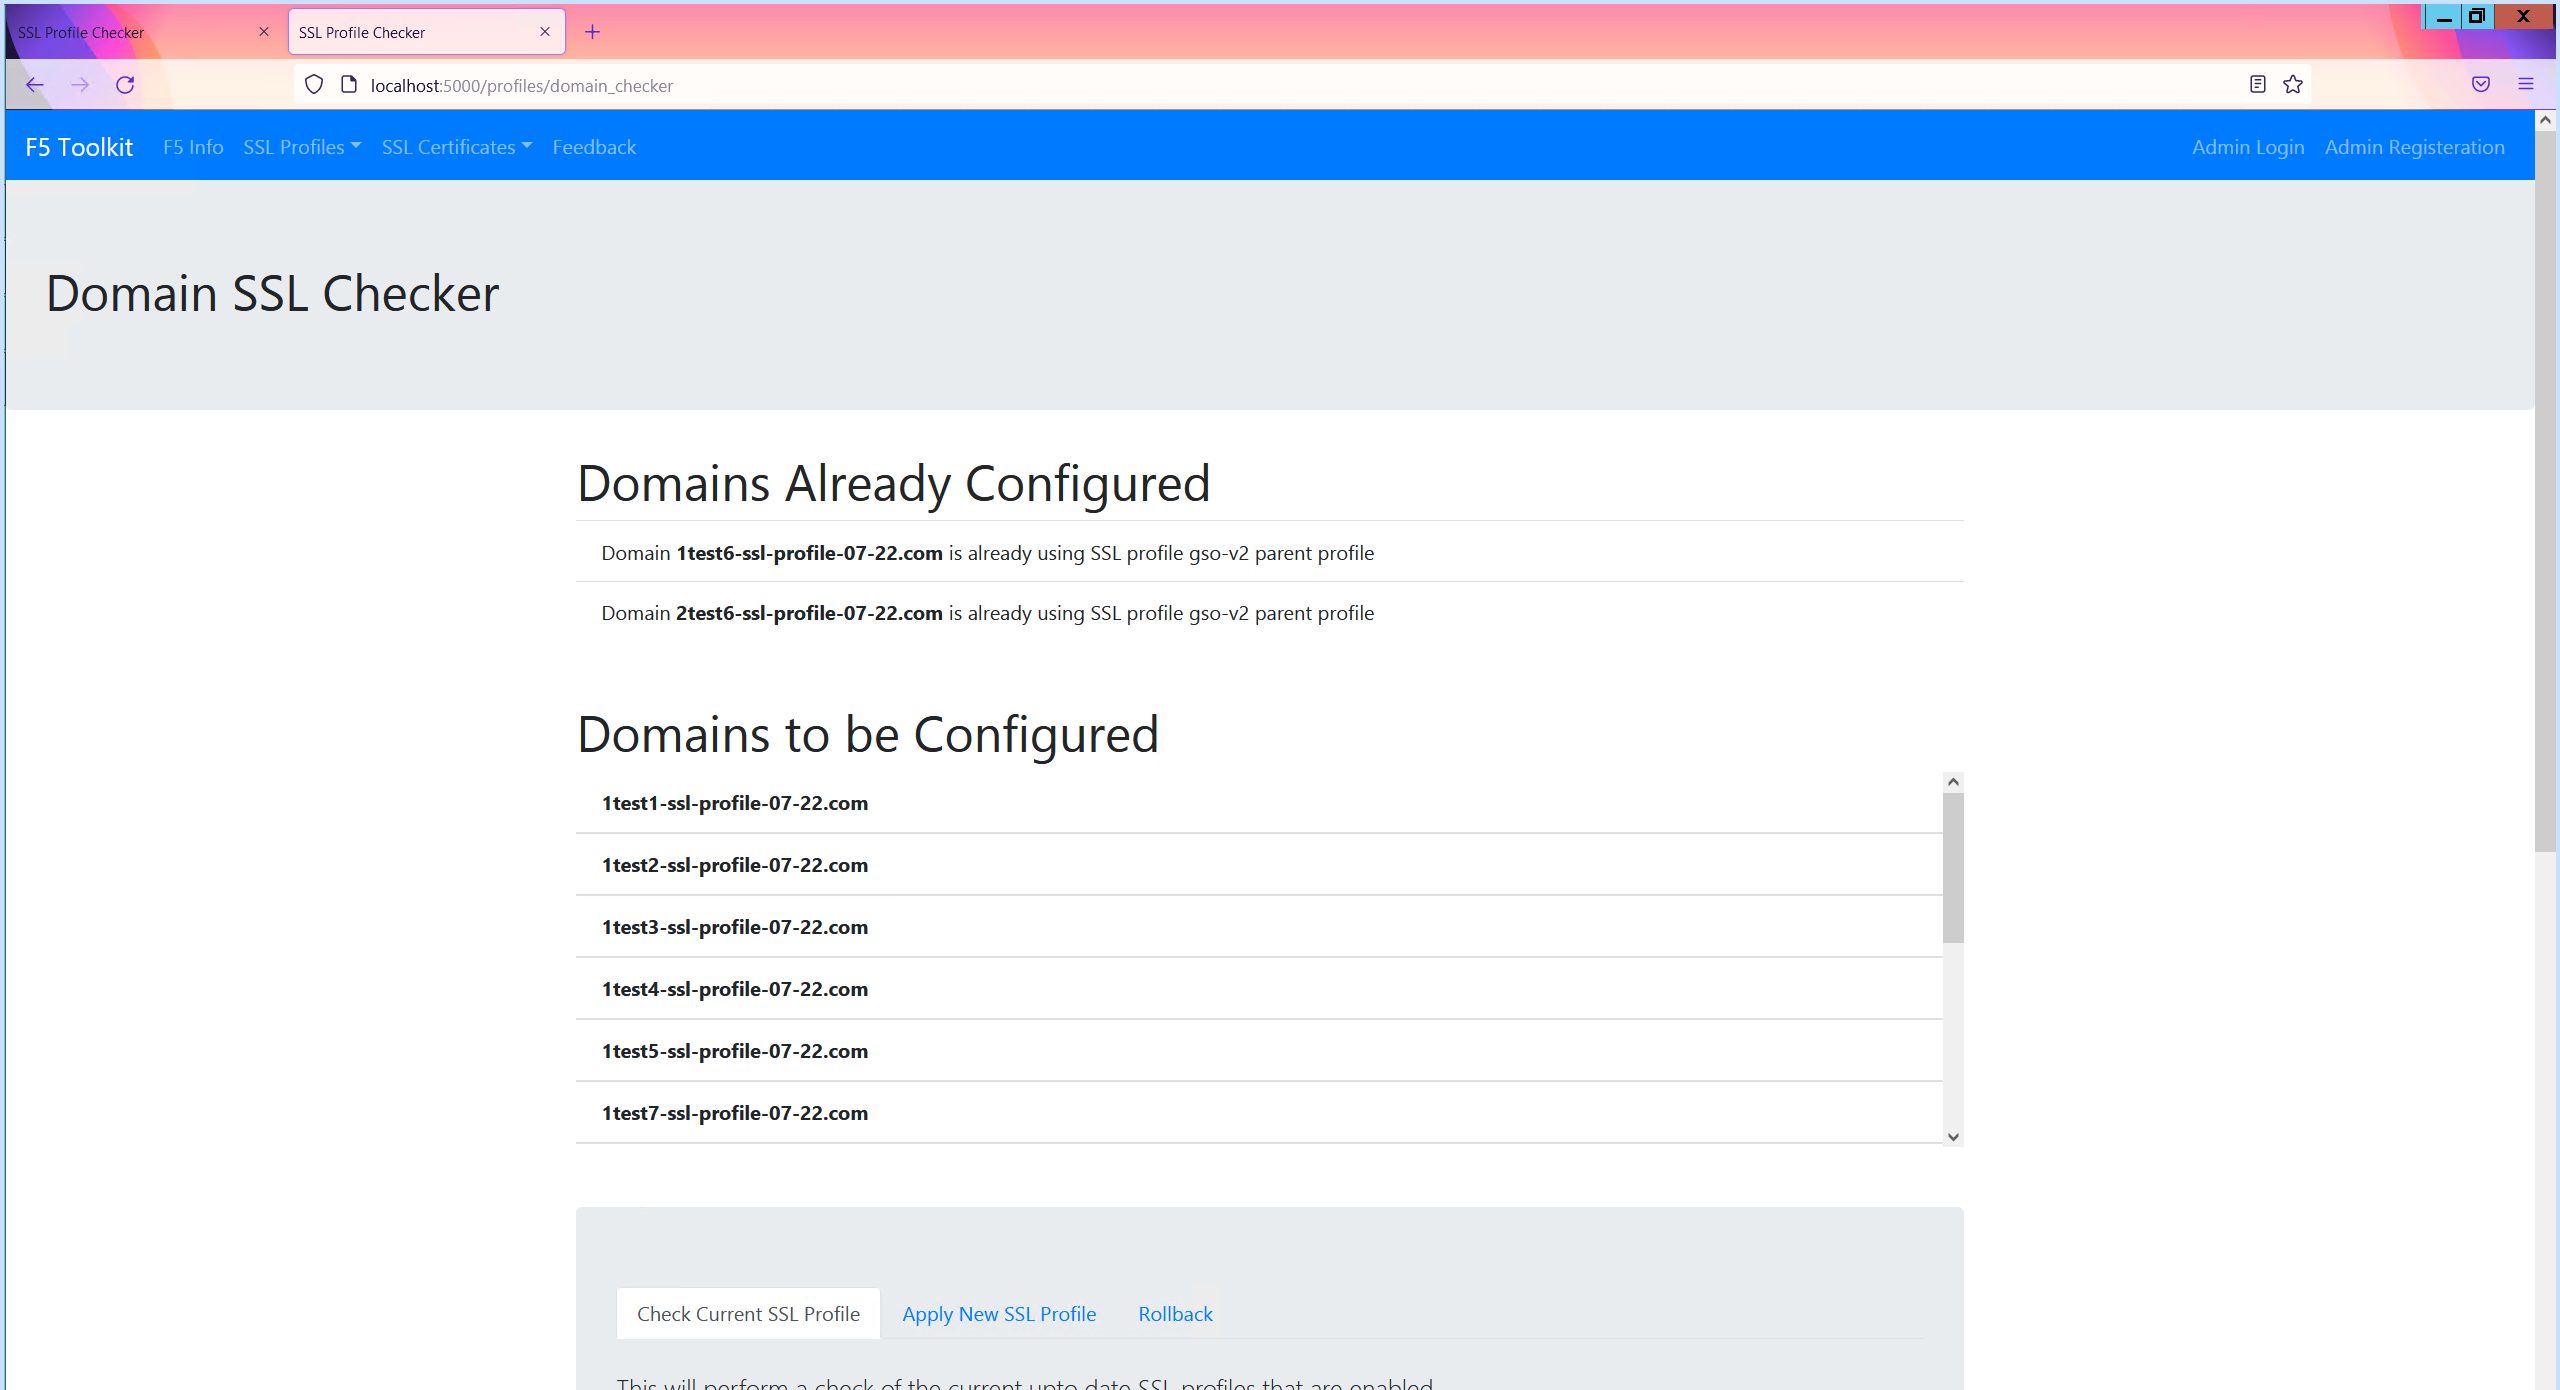
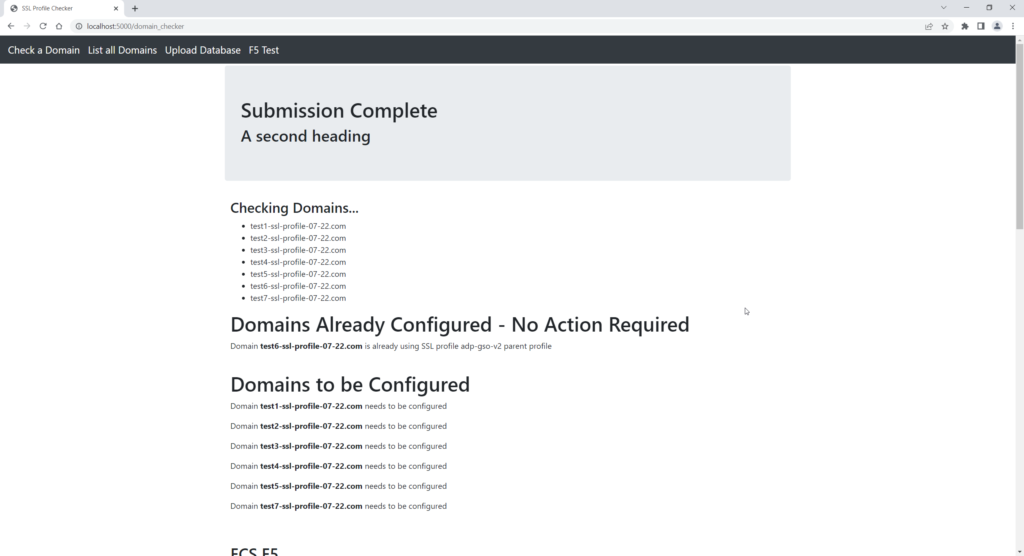
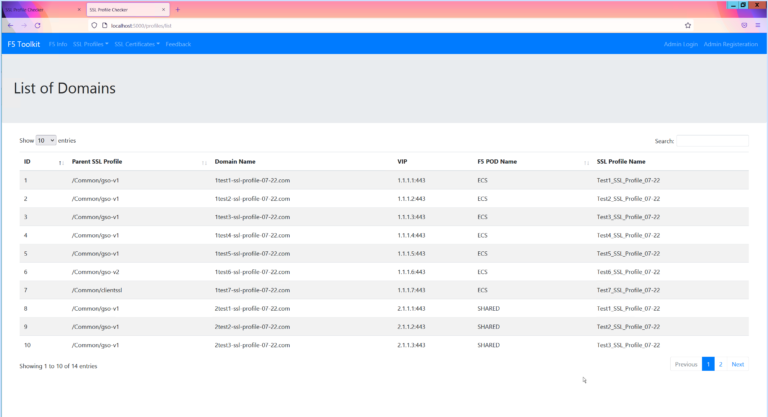
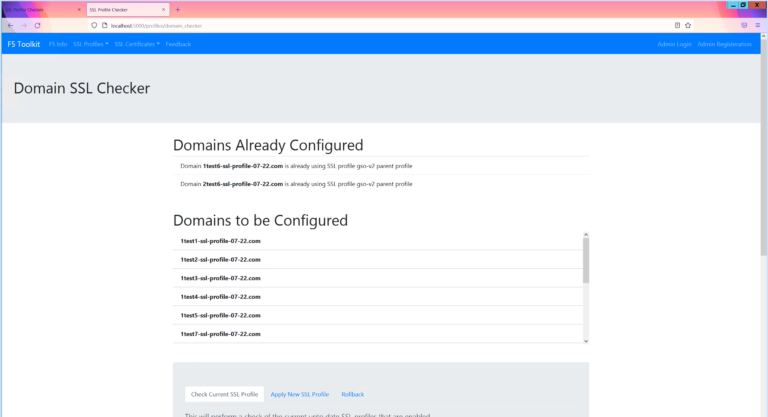
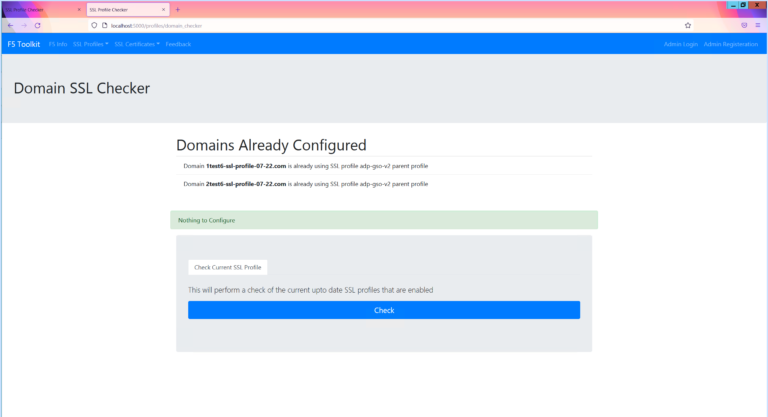
Now that the database is up to date, we can check domains. The SSL parent profile should be gso-v2.
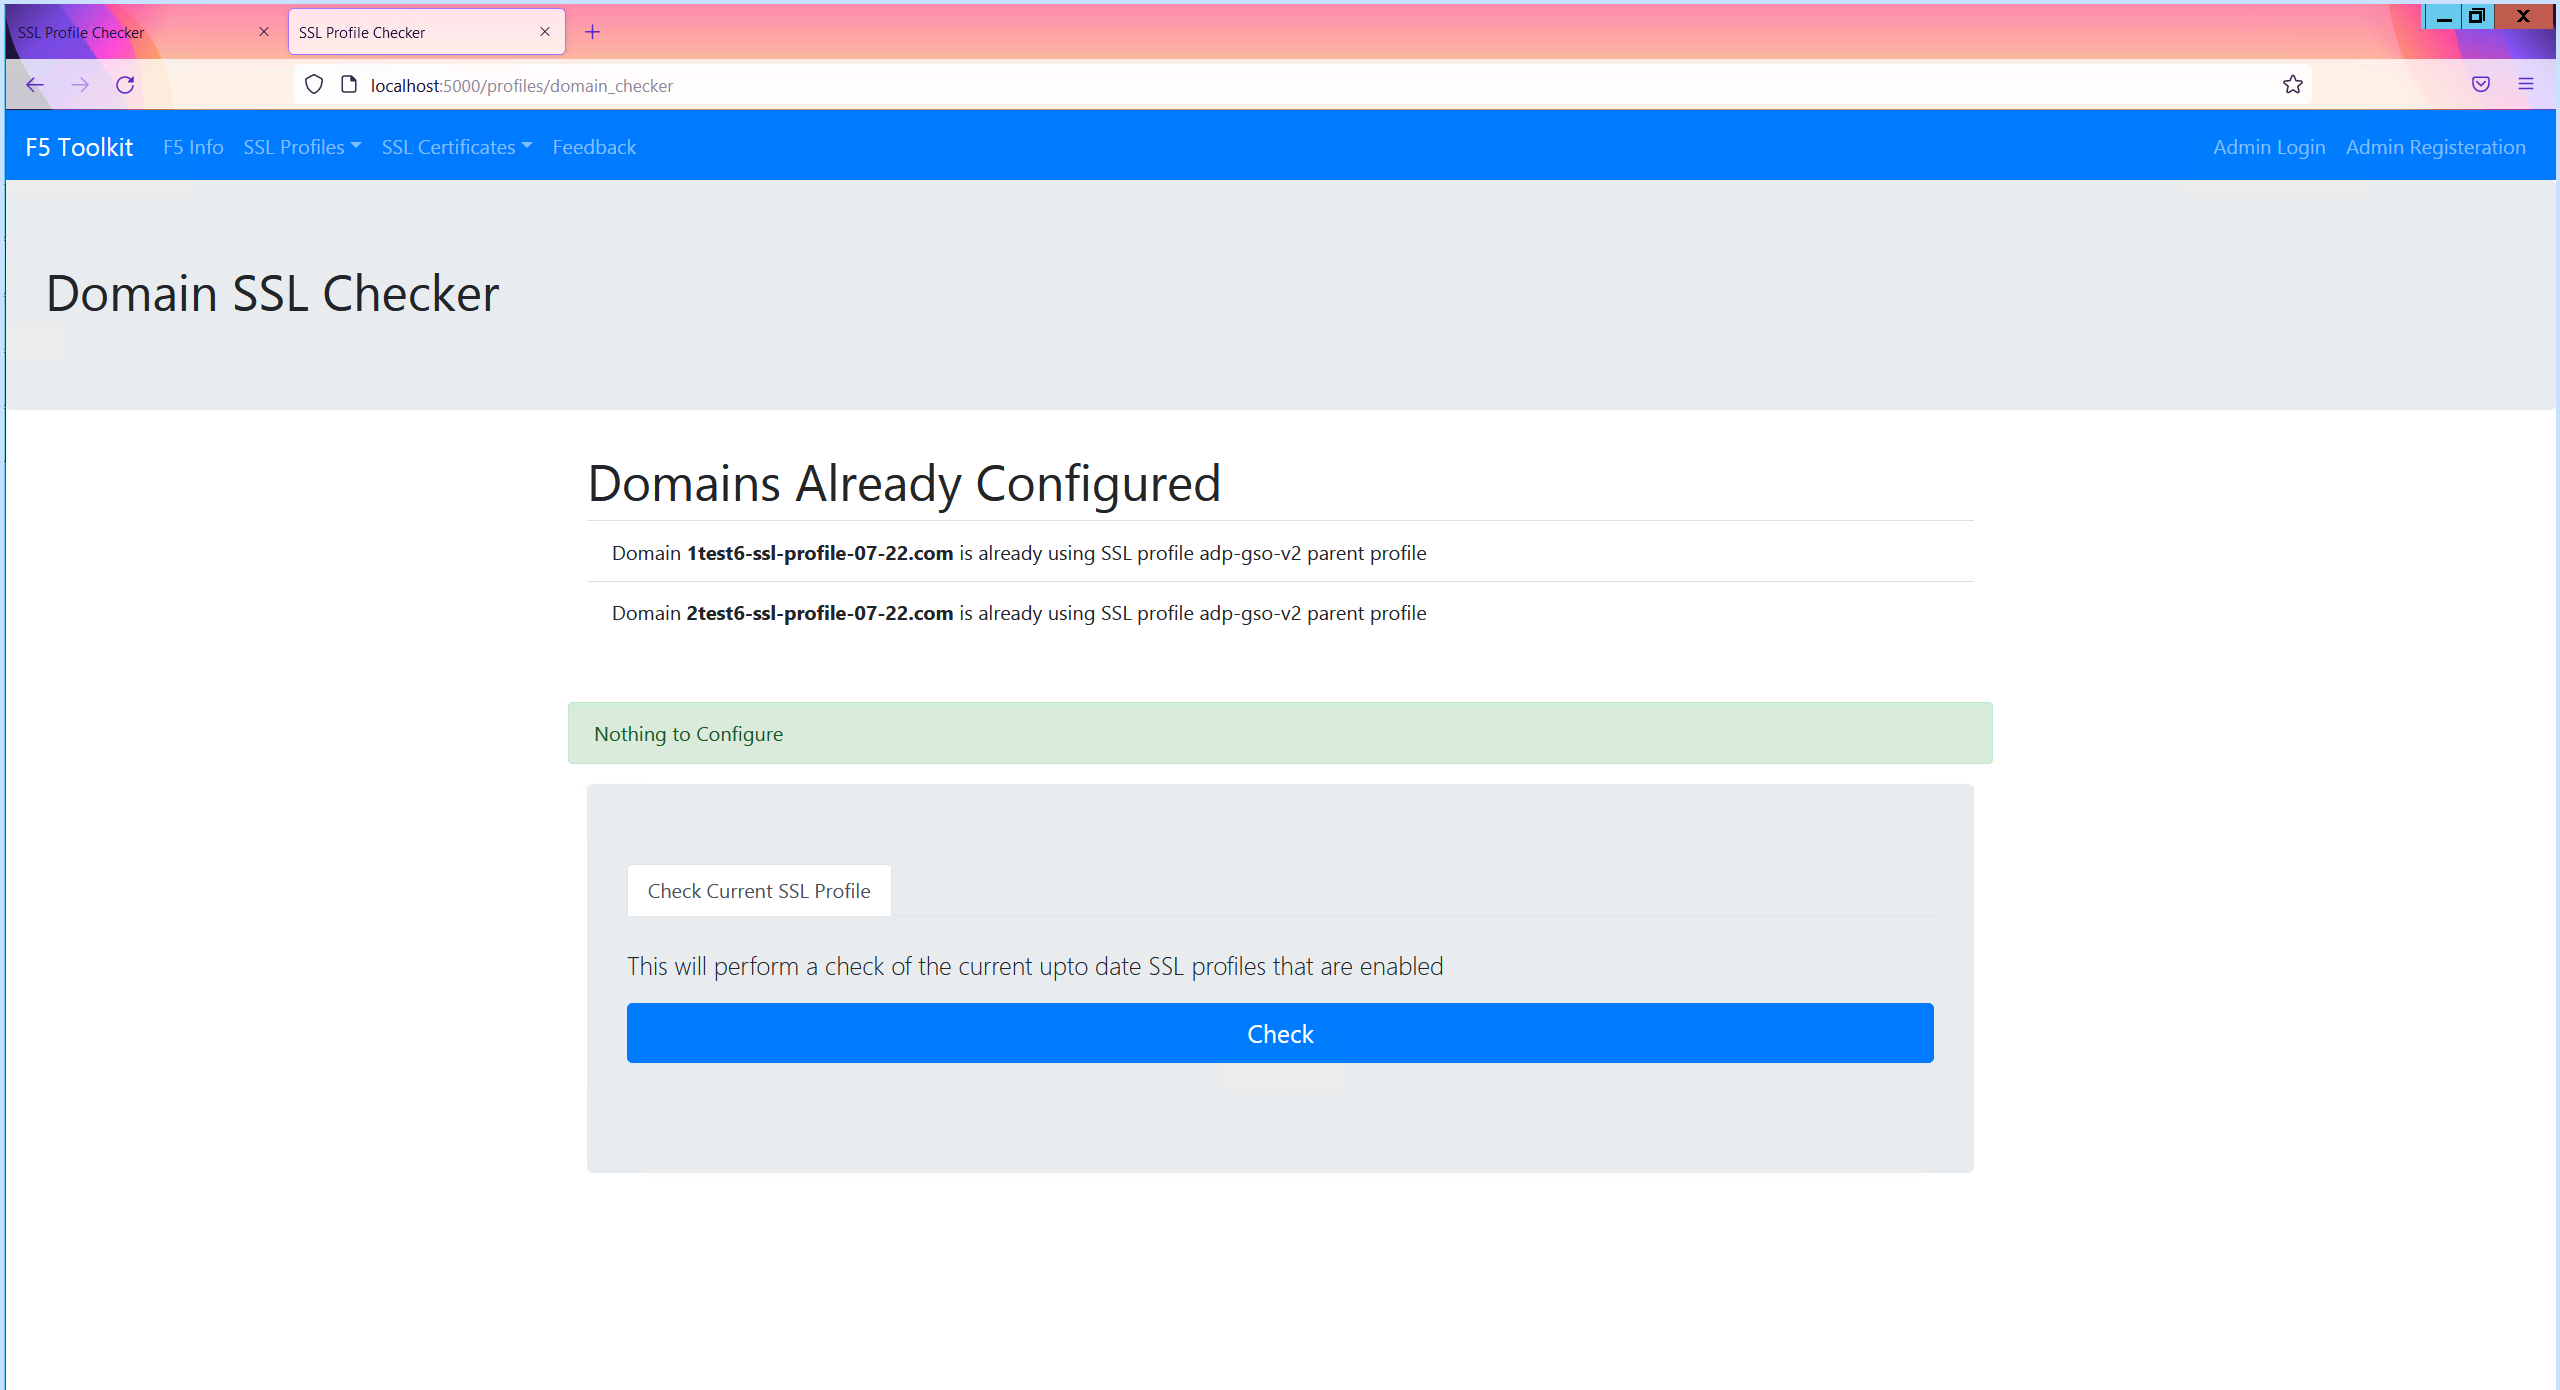
As you can see from the domain list screenshot, we have two already correctly configured. These are ignored and removed from any configuration.
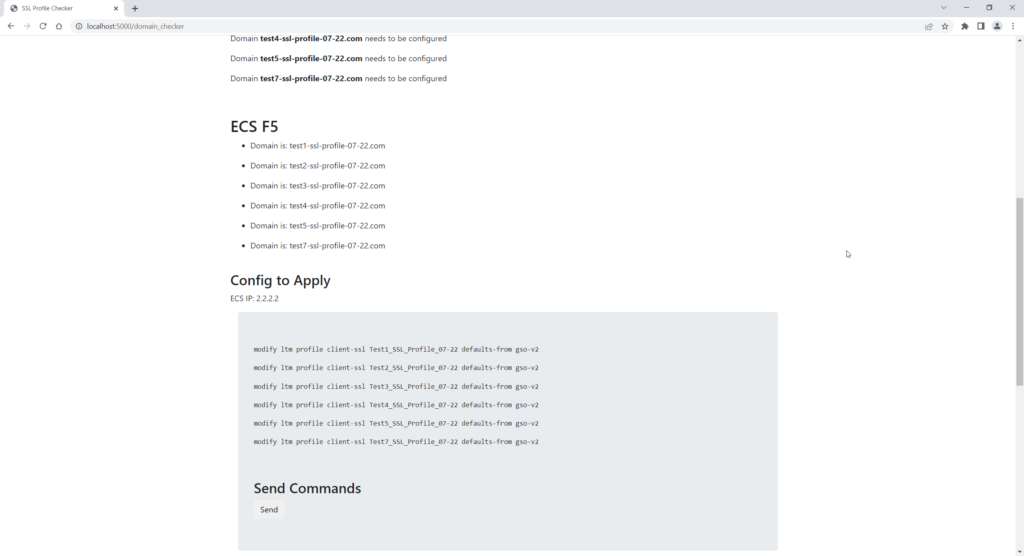
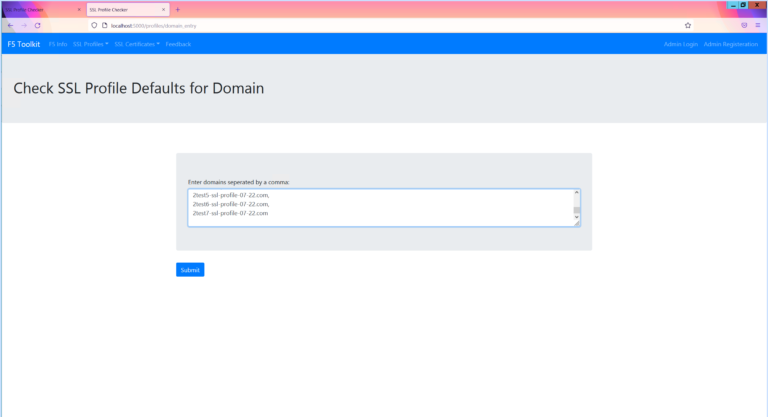
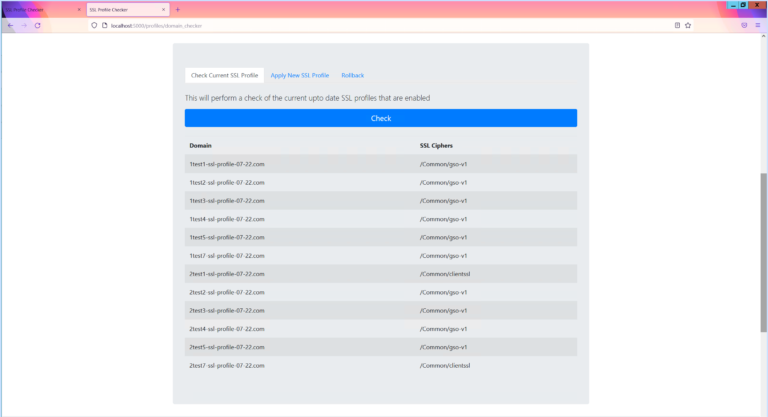
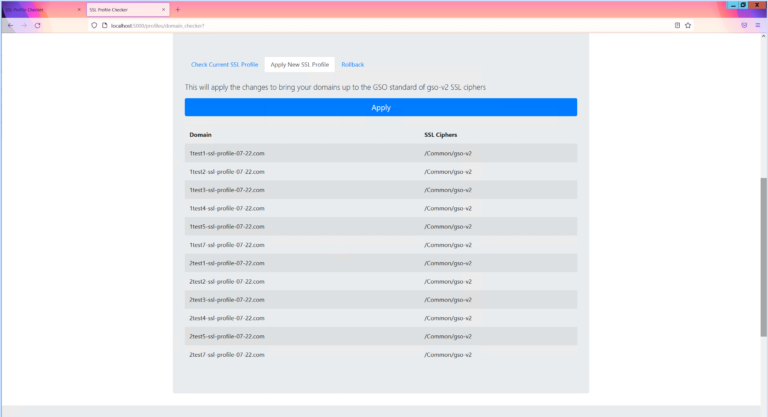
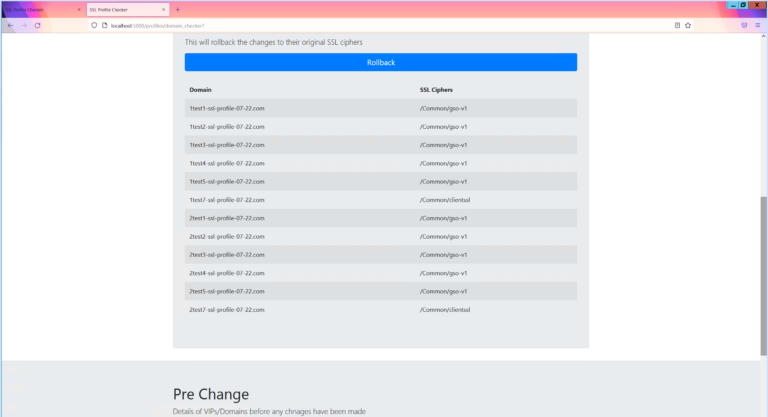
There are three tabs; Check, Configuration and Rollback.
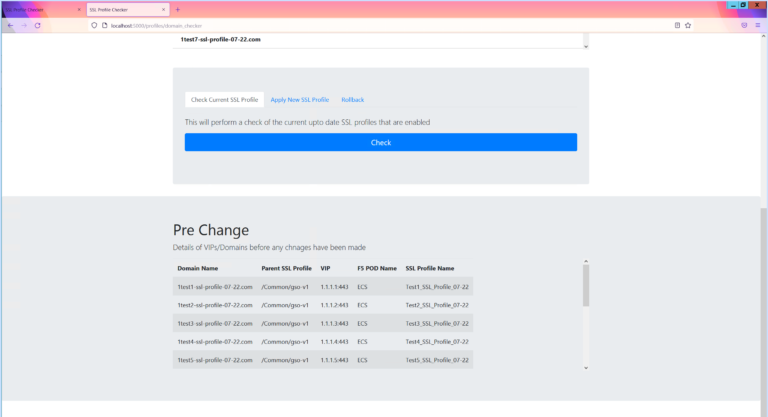
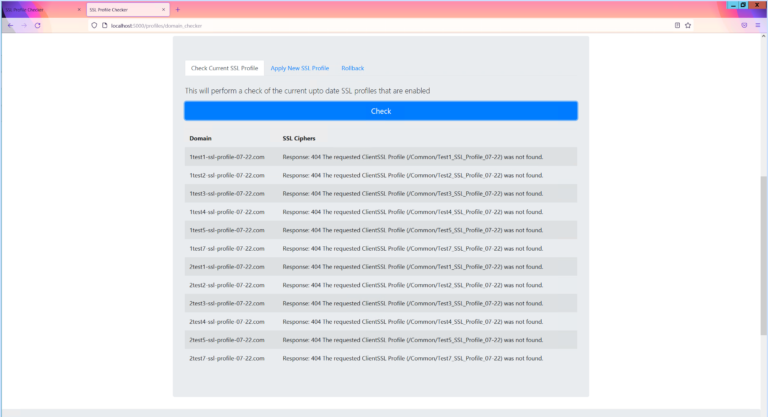
Check
The Check tab performs and GET request to each F5 and their respective SSL profiles. Pulls them back and says the current status. This is helpful as the database is currently updated manually.
If the F5 cannot be reached or there is no such SSL profile the response from the F5 will be listed instead of the expected SSL profile output.
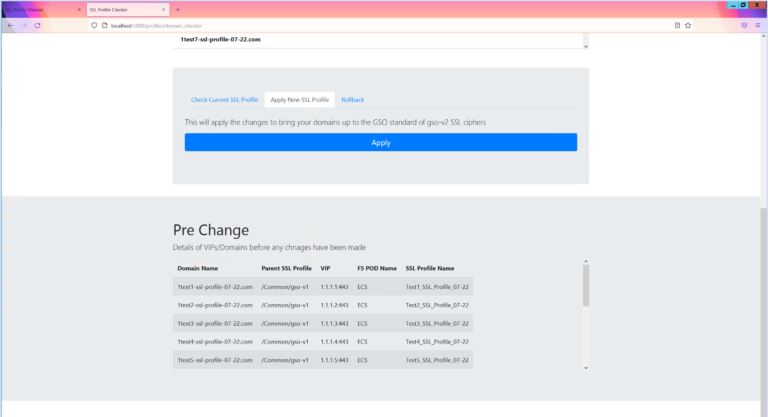
Configuration
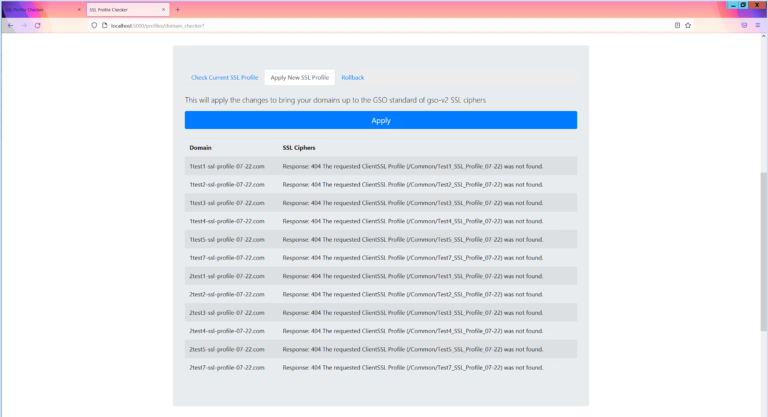
The Configuration tab is what applies the correct gso-v2 parent profile to each of the SSL profile.
Again, if the F5 cannot be reached or there is no such SSL profile the response from the F5 will be listed instead of the expected SSL profile output.
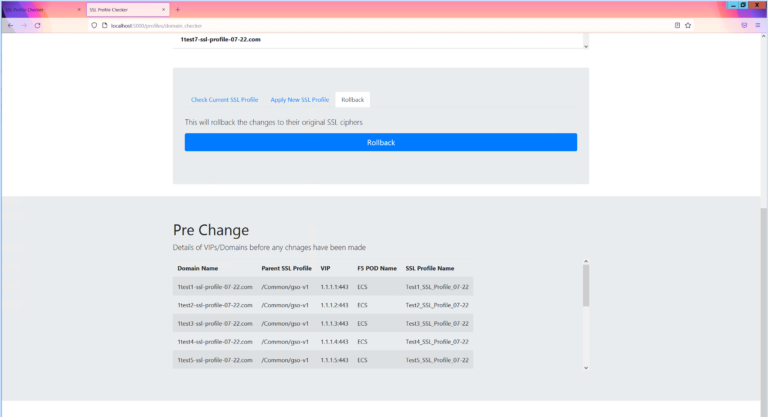
Rollback
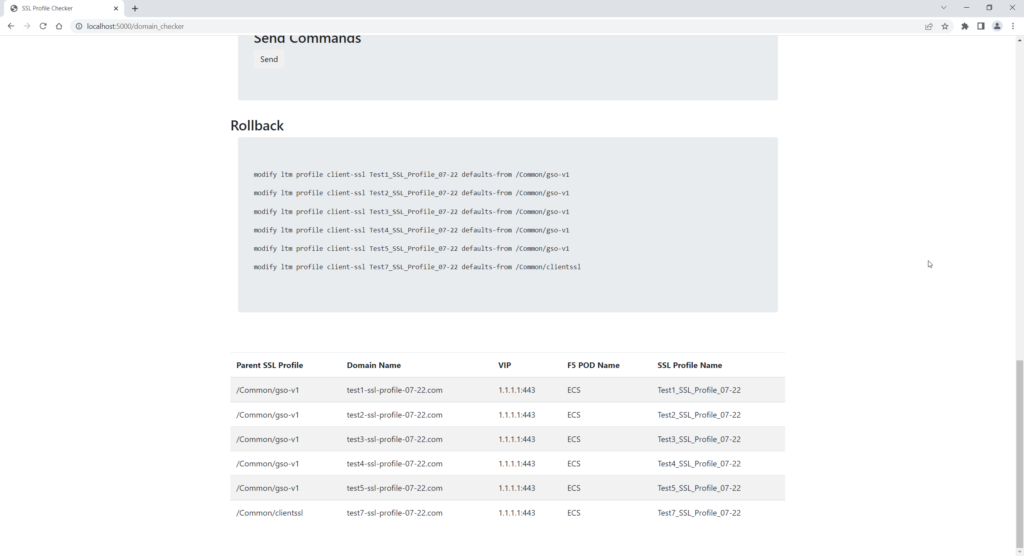
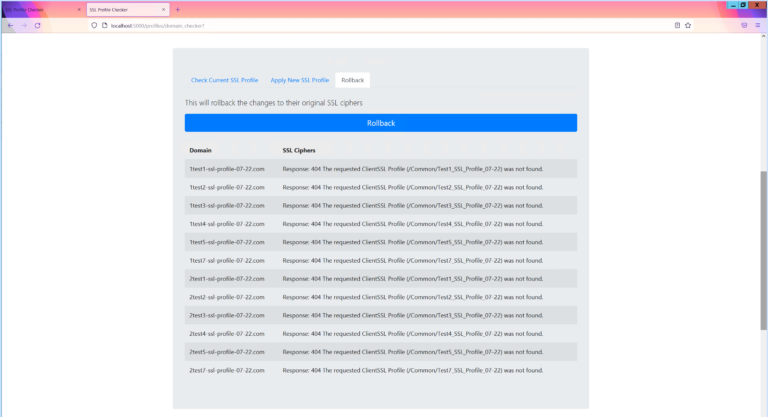
This is the same as the Configuration Tab, except it performs a rollback to how the SSL profiles was before any of this started.
It will look exactly the same as in the pre change table at the bottom of the page.
See the database setup workflow4 screenshots
Upload and refresh the database before checking SSL profiles.
See checks, configuration and rollback12 screenshots
Compare the three workflows, including missing profiles and domains that are already configured.
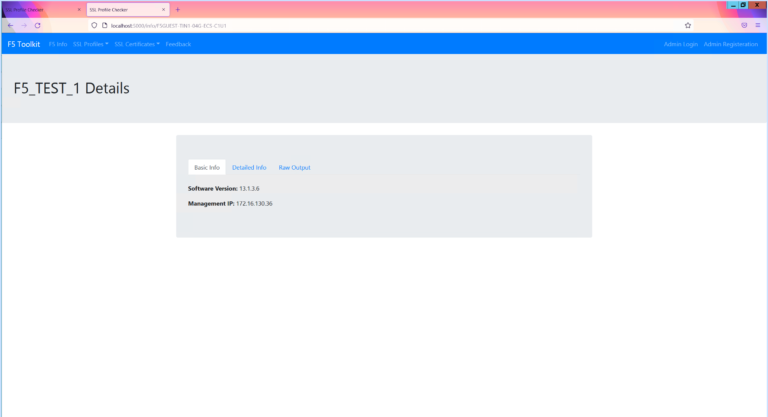
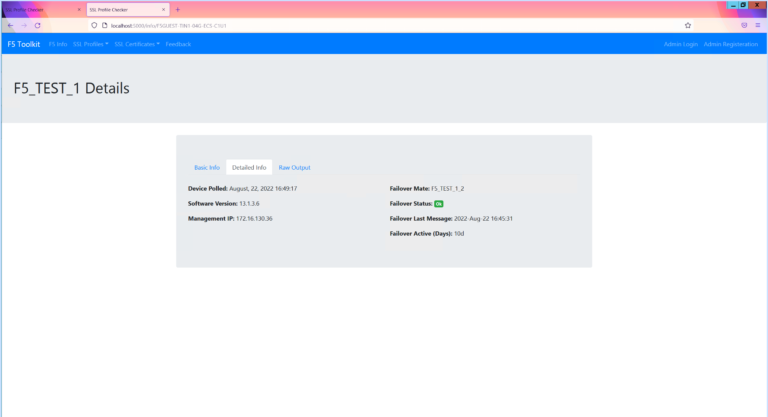
Gather F5 Info
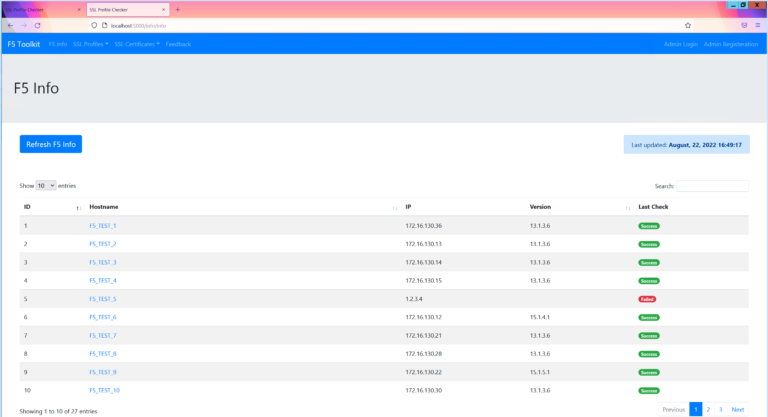
This is to perform the task of gathering basic F5 information that is easily available to users. The process works by using a list of F5 management IP addresses to send a couple of API requests for basic info.
- Hostname
- Software Version
- Failover Details
From this I have constructed a main page, with links to more detailed information. I’ll detail the process of this and link to it.
The button at the top of the table is what performs the series of API requests against the F5 management IP list. The date of last updated is also displayed for a user to easily see.
All of this is stored in a database table. Each refresh deletes and updates the table.
F5s cannot be individually refreshed. It is an all or none function.
See the F5 inventory views4 screenshots
Move from the inventory table into individual F5 details and code output.
F5 Certificates
This is probably the most complicated part. For a start there are two options.
- Generate SSL certificate only
- Generate SSL certificate, create a new VIP, pool and add members to the pool
Generate SSL Certificate only
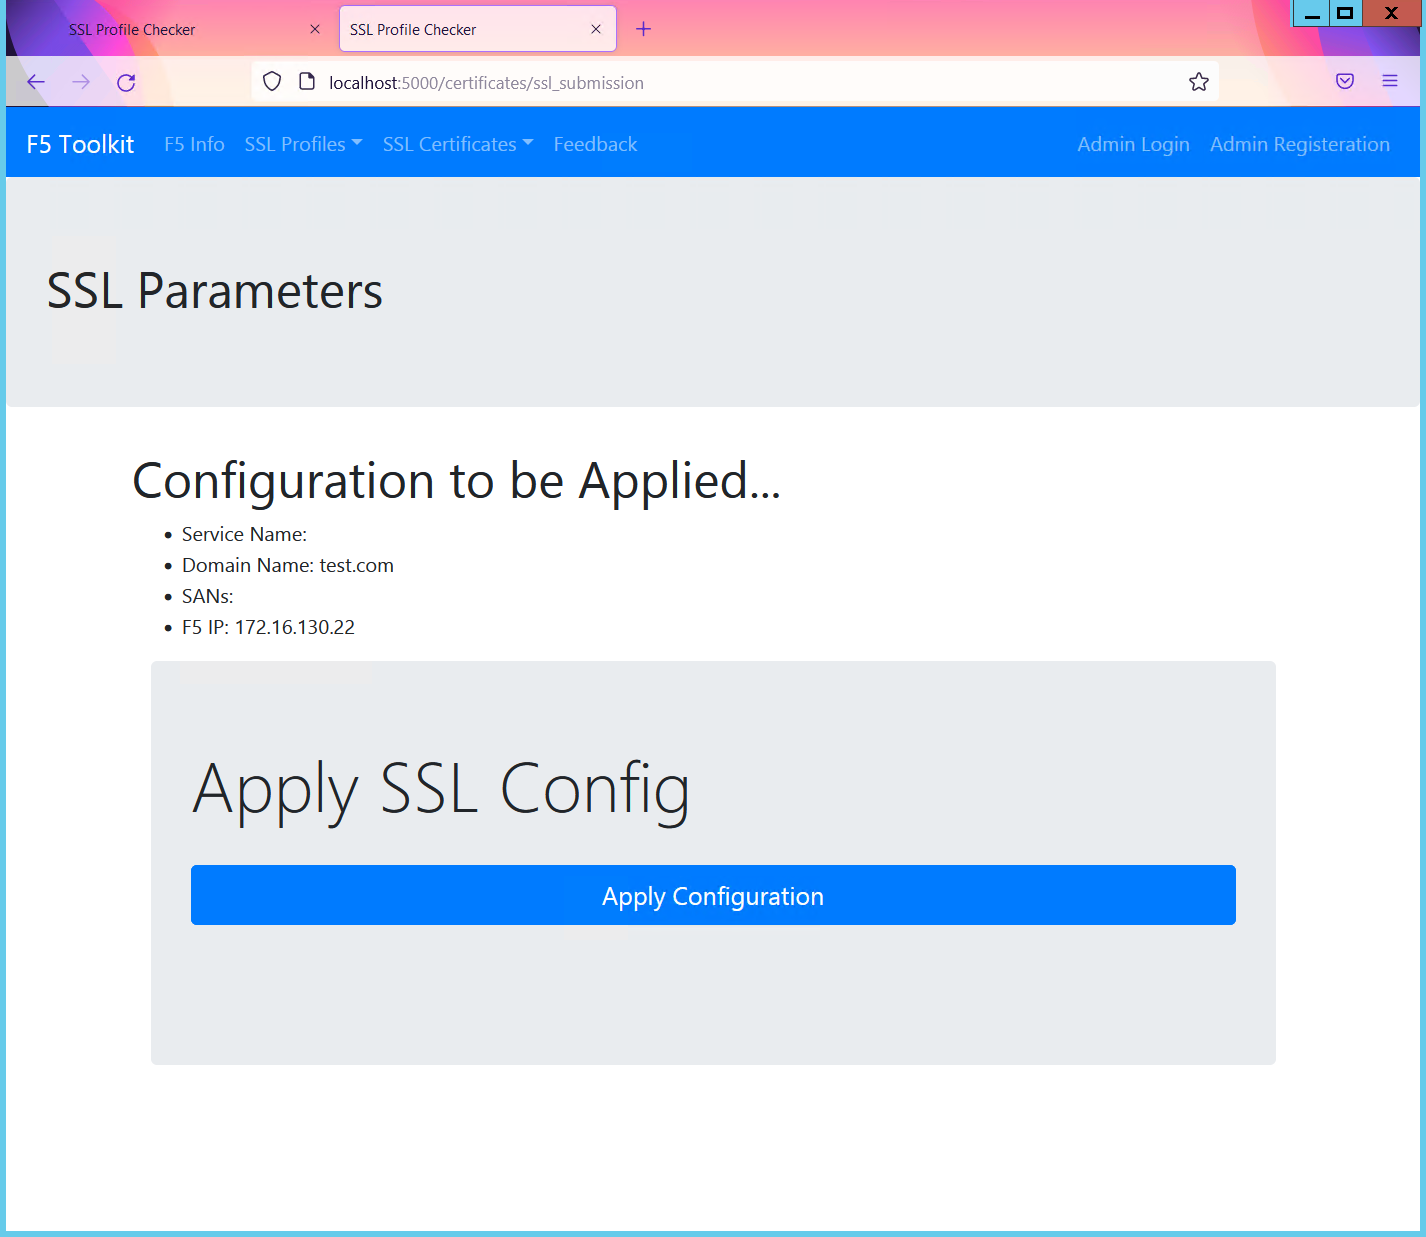
There is a form to ask the user the; domain name, any SANs and the F5 management IP.
What will happen is the SSL certificate will be created and signed by a third-party CA using their own API. That certificate will then be uploaded to the F5 specified in the form. This is then available for an administrator to create or add to an existing SSL profile to then use.
Generate SSL Certificate and F5 Changes
This is where we run through the exact same process to generate the SSL certificate, and upload that to the F5 specified.
The extra parts here are to take the extra fields in the form to create a new VIP, pool members and SSL redirect required.
See the certificate forms2 screenshots
The forms for certificate generation and the additional VIP and pool configuration.

Implementation notes
For this project I needed to utilise different technologies that I had not used before in any depth; databases, jQuery, HTML being the main ones.
I’ll go through and create a few posts to detail some of the parts I found more complicated.