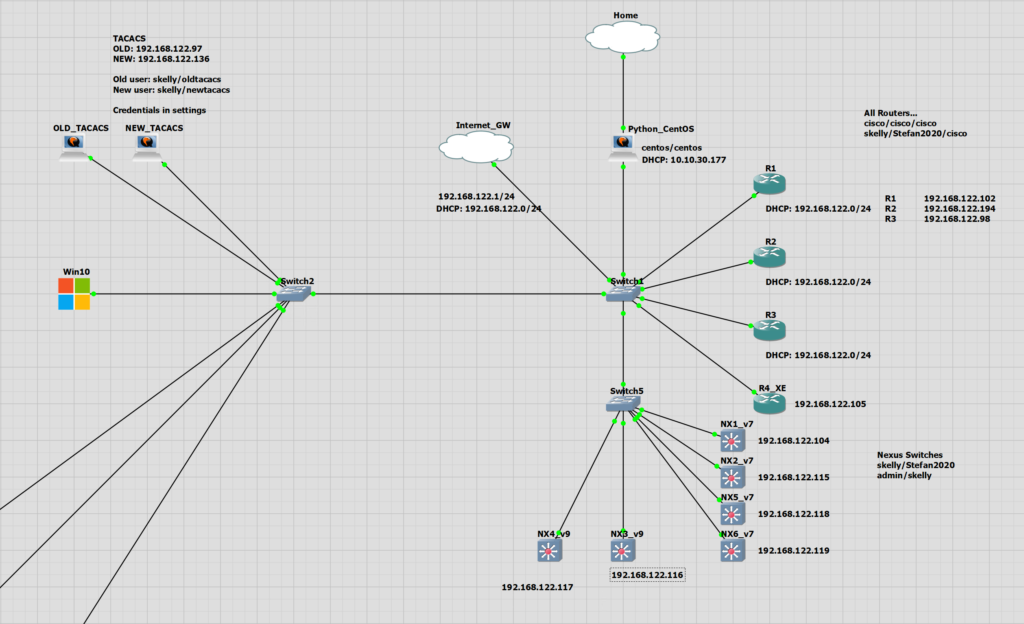
The Original Lab
Original Scripts
A link to the original scripts in this example may be found on my GitHub.
The script takes in a CSV already created that has the IP, hostname, and username. It is like this as this file was created from another script for when you have multiple devices with different usernames. This other script allowed you to test multiple credentials per device and when one worked made added that to a list to be written out to a CSV.
Back to the TACACS script, this will try to login with one of three credentials create a file named iosxe_tacacs_check_modify_config.csv
It will contain the config to remove AAA and TACACS.
This file will be used by the second script along with a configuration file. So script 2 will; login, remove old config and add in the new config.
The example script below is for IOS devices only, as the config is slightly different for different software versions I have other scripts for; NXOS, IOS, IOSXE I split them up.
When I was testing this out to write the lab up, I had several problems with the scripts. They are quite difficult to use, nothing that can easily be given to anyone to configure. This will need to be fixed!
Device List CSV
(.venv) -bash-4.2$ cat cisco_check_ssh_usernames_output.csvIP Address,Hostname,Username192.168.122.102,R1,admin192.168.122.194,R2,skelly192.168.122.98,R3,adminUsername/Password List
Local: cisco/ciscoLocal: admin/Stefan2020OLD_TACACS: skelly/Stefan2020Running Script 1
(.venv) -bash-4.2$ python ios-xe_a1_check_modify_tacacs.pyPlease Enter your TACACS passwordPassword:Please Enter admin passwordPassword:Please Enter cisco passwordPassword:These are the devices that we will be connecting to...IP Address: 192.168.122.102IP Address: 192.168.122.194IP Address: 192.168.122.98SSH connection established to 192.168.122.102:22Interactive SSH session establishedHostname: R1IP Address: 192.168.122.102Getting AAA & TACACSClosing connection##############################SSH connection established to 192.168.122.194:22Interactive SSH session establishedHostname: R2IP Address: 192.168.122.194Getting AAA & TACACSClosing connection##############################SSH connection established to 192.168.122.98:22Interactive SSH session establishedHostname: R3IP Address: 192.168.122.98Getting AAA & TACACSClosing connection##############################CSV written outScript 1 output
| IP Address | Hostname | Username | Current Config | Removal Configuration |
| 192.168.122.102 | R1 | admin |
aaa new-modelaaa session-id common |
no aaa session-id common |
| 192.168.122.194 | R2 | skelly |
aaa new-modelaaa authentication login IPCISCOAUTH group tacacs+ local |
no aaa authentication login IPCISCOAUTH group tacacs+ localno aaa authorization exec default group tacacs+ |
| 192.168.122.98 | R3 | admin |
aaa new-model |
no aaa session-id common |
Script 2
Script 2 is used to; login, remove old config and add in the new config. If all goes well then the password for R2 skelly TACACS user should be “newtacacs”.
aaa new-modelaaa session-id commonaaa authentication login IPCISCOAUTH group tacacs+ localtacacs server NEWTACACSaddress ipv4 192.168.122.136key 123abcline vty 0 15login authentication IPCISCOAUTHaaa authorization exec default group tacacs+aaa accounting exec default start-stop group tacacs+Script 2 Output
(.venv) -bash-4.2$ python ios-xe_a2_config_tacacs_dynamic-config.pyPlease Enter your TACACS passwordPassword:Please Enter admin passwordPassword:Please Enter the cisco user passwordPassword:Please enter the file name of the config file to apply to devices: newtacacs.cfgThese are the devices that we will be connecting to...IP Address: 192.168.122.102IP Address: 192.168.122.194IP Address: 192.168.122.98SSH connection established to 192.168.122.102:22Interactive SSH session establishedConfig file to be appliedaaa new-modelaaa session-id commonaaa authentication login IPCISCOAUTH group tacacs+ localtacacs server NEWTACACSaddress ipv4 192.168.122.136key 123abcline vty 0 15login authentication IPCISCOAUTHaaa authorization exec default group tacacs+aaa accounting exec default start-stop group tacacs+Hostname: R1IP Address: 192.168.122.102Entering the config mode ...Removing config...no aaa session-id commonRemoval Complete...Applying config...Config Complete...Preparing output...Getting TACACSClosing connection##############################SSH connection established to 192.168.122.194:22Interactive SSH session establishedConfig file to be appliedaaa new-modelaaa session-id commonaaa authentication login IPCISCOAUTH group tacacs+ localtacacs server NEWTACACSaddress ipv4 192.168.122.136key 123abcline vty 0 15login authentication IPCISCOAUTHaaa authorization exec default group tacacs+aaa accounting exec default start-stop group tacacs+Hostname: R2IP Address: 192.168.122.194Entering the config mode ...Removing config...no aaa authentication login IPCISCOAUTH group tacacs+ localno aaa authorization exec default group tacacs+no aaa accounting exec default start-stop group tacacs+no aaa session-id commonno tacacs-server host 192.168.122.97 key 123abcRemoval Complete...Applying config...Config Complete...Preparing output...Getting TACACSClosing connection##############################SSH connection established to 192.168.122.98:22Interactive SSH session establishedConfig file to be appliedaaa new-modelaaa session-id commonaaa authentication login IPCISCOAUTH group tacacs+ localtacacs server NEWTACACSaddress ipv4 192.168.122.136key 123abcline vty 0 15login authentication IPCISCOAUTHaaa authorization exec default group tacacs+aaa accounting exec default start-stop group tacacs+Hostname: R3IP Address: 192.168.122.98Entering the config mode ...Removing config...no aaa session-id commonRemoval Complete...Applying config...Config Complete...Preparing output...Getting TACACSClosing connection##############################CSV written outNew TACACS Testing
| IP Address | Hostname | TACACS |
| 192.168.122.102 | R1 | aaa new-model aaa authentication login IPCISCOAUTH group tacacs+ local aaa authorization exec default group tacacs+ aaa accounting exec default start-stop group tacacs+ aaa session-id common tacacs server NEWTACACS |
| 192.168.122.194 | R2 | aaa new-model aaa authentication login IPCISCOAUTH group tacacs+ local aaa authorization exec default group tacacs+ aaa accounting exec default start-stop group tacacs+ aaa session-id common tacacs server NEWTACACS |
| 192.168.122.98 | R3 | aaa new-model aaa authentication login IPCISCOAUTH group tacacs+ local aaa authorization exec default group tacacs+ aaa accounting exec default start-stop group tacacs+ aaa session-id common tacacs server NEWTACACS |
R1#test aaa group tacacs+ skelly newtacacs new-codeSending passwordUser successfully authenticatedUSER ATTRIBUTESusername 0 "skelly"reply-message 0 "Password: "R2#test aaa group tacacs+ skelly newtacacs new-codeSending passwordUser successfully authenticatedUSER ATTRIBUTESusername 0 "skelly"reply-message 0 "Password: "R3#test aaa group tacacs+ skelly newtacacs new-codeSending passwordUser successfully authenticatedUSER ATTRIBUTESusername 0 "skelly"reply-message 0 "Password: "